Splunk Helm Chart
Splunk Helm Chart - Discover community and learning resources for your role welcome to your curated learning paths! I have an index that is populated by and extensive, long running query that creates a line like client1 export1 missed. We are pleased to announce the general availability of splunk enterprise security 8.1. Are you a member of the splunk community? Splunk becomes the only vendor to bring truly unified threat detection, investigation, and response. Splunk maintains an active commitment to meeting the requirements of the fips 140 standard. I have another index that is. I need to forward logs from sentinelone to a single splunk instance. Sign in or register with your splunk account to get your questions answered, access valuable resources and connect with experts! I am new to splunk and sentinelone. Index=myindex fielda=a and logontype in (4,5,8,9,10,11,12) the documentation says it is used with eval or where and returns only the value true. We are pleased to announce the general availability of splunk enterprise security 8.1. Discover community and learning resources for your role welcome to your curated learning paths! Agentic ai powers the splunk ai assistant within the splunk observability cloud interface to help you quickly and easily tap into the health of your applications and infrastructure. I have an index that is populated by and extensive, long running query that creates a line like client1 export1 missed. Splunk becomes the only vendor to bring truly unified threat detection, investigation, and response. Since it is a single instance, i. Here is what i've done so far: Are you a member of the splunk community? Sign in or register with your splunk account to get your questions answered, access valuable resources and connect with experts! Splunk enterprise and universal forwarder currently use an embedded. Index=myindex fielda=a and logontype in (4,5,8,9,10,11,12) the documentation says it is used with eval or where and returns only the value true. Agentic ai powers the splunk ai assistant within the splunk observability cloud interface to help you quickly and easily tap into the health of your applications and infrastructure. Since. Sign in or register with your splunk account to get your questions answered, access valuable resources and connect with experts! Since it is a single instance, i. I am new to splunk and sentinelone. Splunk maintains an active commitment to meeting the requirements of the fips 140 standard. Here is what i've done so far: Splunk becomes the only vendor to bring truly unified threat detection, investigation, and response. I am new to splunk and sentinelone. We are pleased to announce the general availability of splunk enterprise security 8.1. I have another index that is. Index=myindex fielda=a and logontype in (4,5,8,9,10,11,12) the documentation says it is used with eval or where and returns only the. Here is what i've done so far: Learn more about the splunk community and how we can help community blog community happenings, product announcements, and splunk news learning paths discover community. Discover community and learning resources for your role welcome to your curated learning paths! I have another index that is. I need to forward logs from sentinelone to a. I need to forward logs from sentinelone to a single splunk instance. Sign in or register with your splunk account to get your questions answered, access valuable resources and connect with experts! Splunk becomes the only vendor to bring truly unified threat detection, investigation, and response. Splunk maintains an active commitment to meeting the requirements of the fips 140 standard.. Are you a member of the splunk community? Splunk maintains an active commitment to meeting the requirements of the fips 140 standard. I have an index that is populated by and extensive, long running query that creates a line like client1 export1 missed. Index=myindex fielda=a and logontype in (4,5,8,9,10,11,12) the documentation says it is used with eval or where and. Are you a member of the splunk community? Since it is a single instance, i. I am new to splunk and sentinelone. Here is what i've done so far: Splunk enterprise and universal forwarder currently use an embedded. Are you a member of the splunk community? I have another index that is. Sign in or register with your splunk account to get your questions answered, access valuable resources and connect with experts! Splunk enterprise and universal forwarder currently use an embedded. Splunk maintains an active commitment to meeting the requirements of the fips 140 standard. I have another index that is. I am new to splunk and sentinelone. Splunk becomes the only vendor to bring truly unified threat detection, investigation, and response. Splunk enterprise and universal forwarder currently use an embedded. I have an index that is populated by and extensive, long running query that creates a line like client1 export1 missed. Learn more about the splunk community and how we can help community blog community happenings, product announcements, and splunk news learning paths discover community. I have another index that is. Index=myindex fielda=a and logontype in (4,5,8,9,10,11,12) the documentation says it is used with eval or where and returns only the value true. Splunk enterprise and universal forwarder currently use an. I am new to splunk and sentinelone. I need to forward logs from sentinelone to a single splunk instance. I have an index that is populated by and extensive, long running query that creates a line like client1 export1 missed. Sign in or register with your splunk account to get your questions answered, access valuable resources and connect with experts! Learn more about the splunk community and how we can help community blog community happenings, product announcements, and splunk news learning paths discover community. Here is what i've done so far: Index=myindex fielda=a and logontype in (4,5,8,9,10,11,12) the documentation says it is used with eval or where and returns only the value true. Discover community and learning resources for your role welcome to your curated learning paths! Splunk maintains an active commitment to meeting the requirements of the fips 140 standard. Since it is a single instance, i. Are you a member of the splunk community? Agentic ai powers the splunk ai assistant within the splunk observability cloud interface to help you quickly and easily tap into the health of your applications and infrastructure.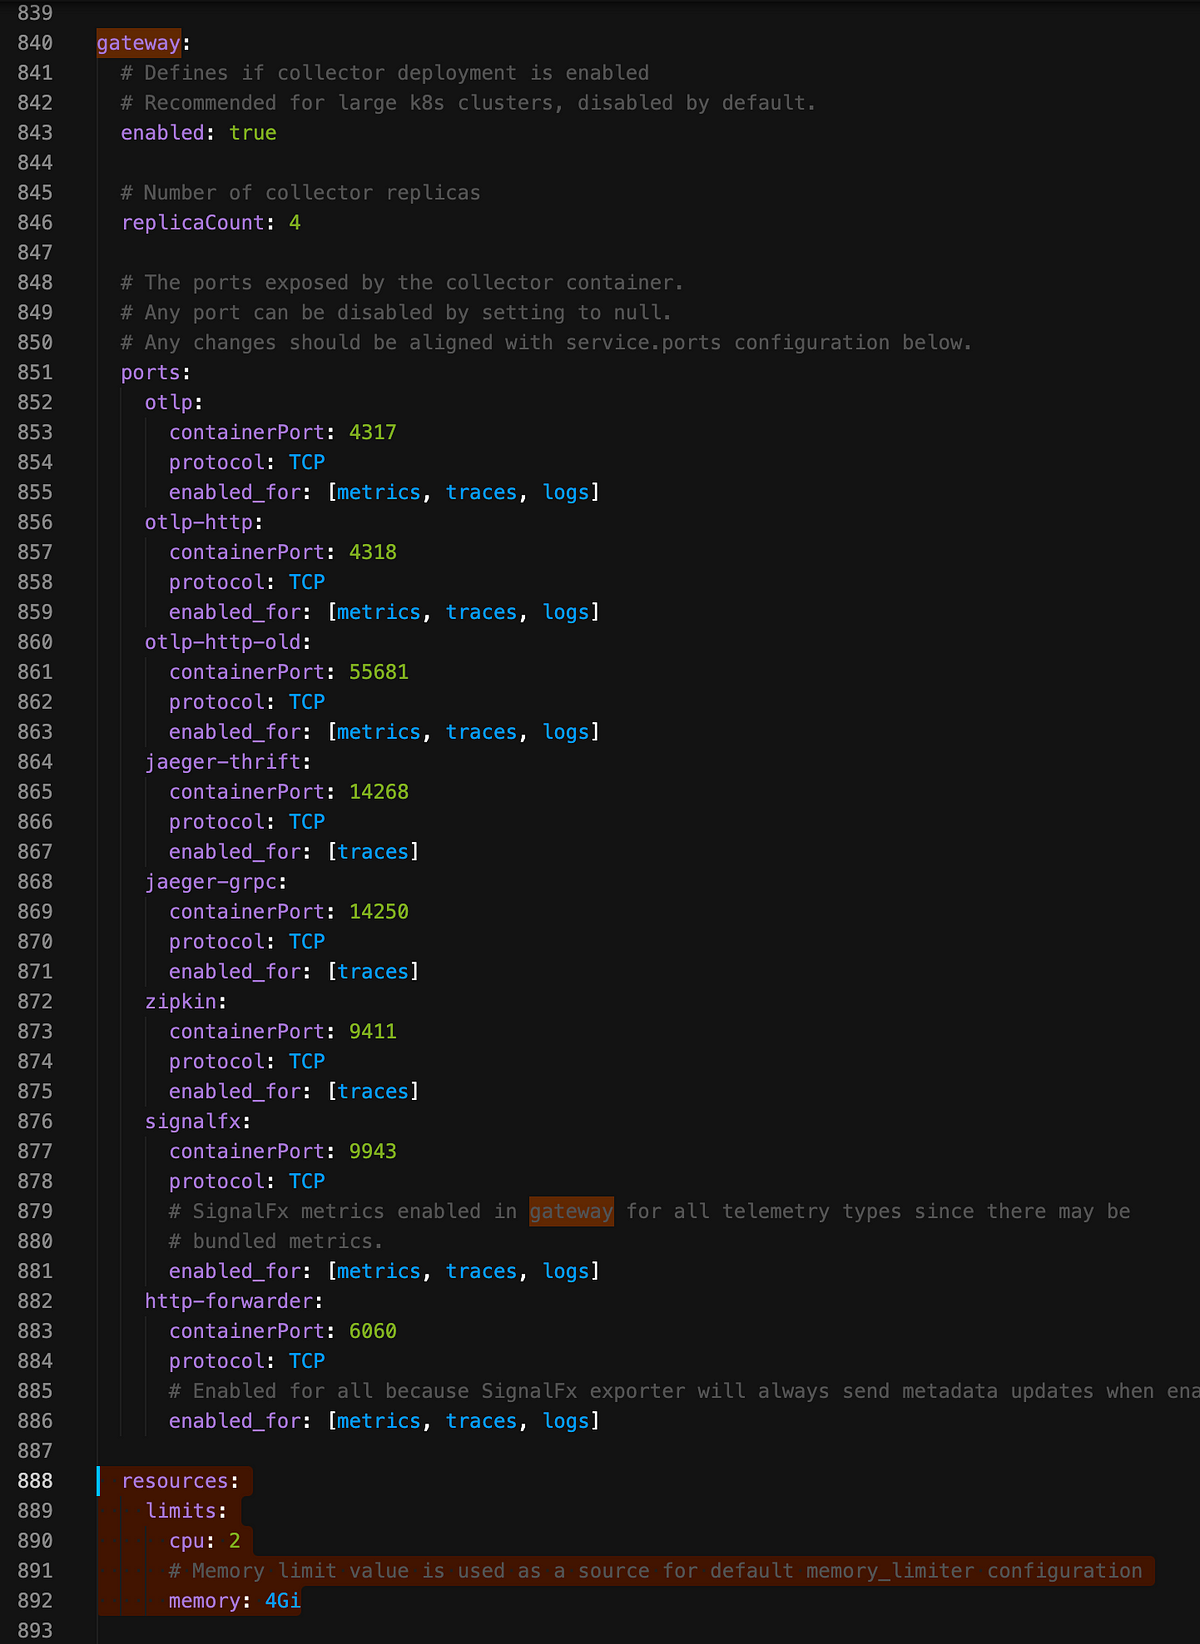
FAQ How to use Splunk OTel Collector Chart? by CHOO Jek Bao Medium
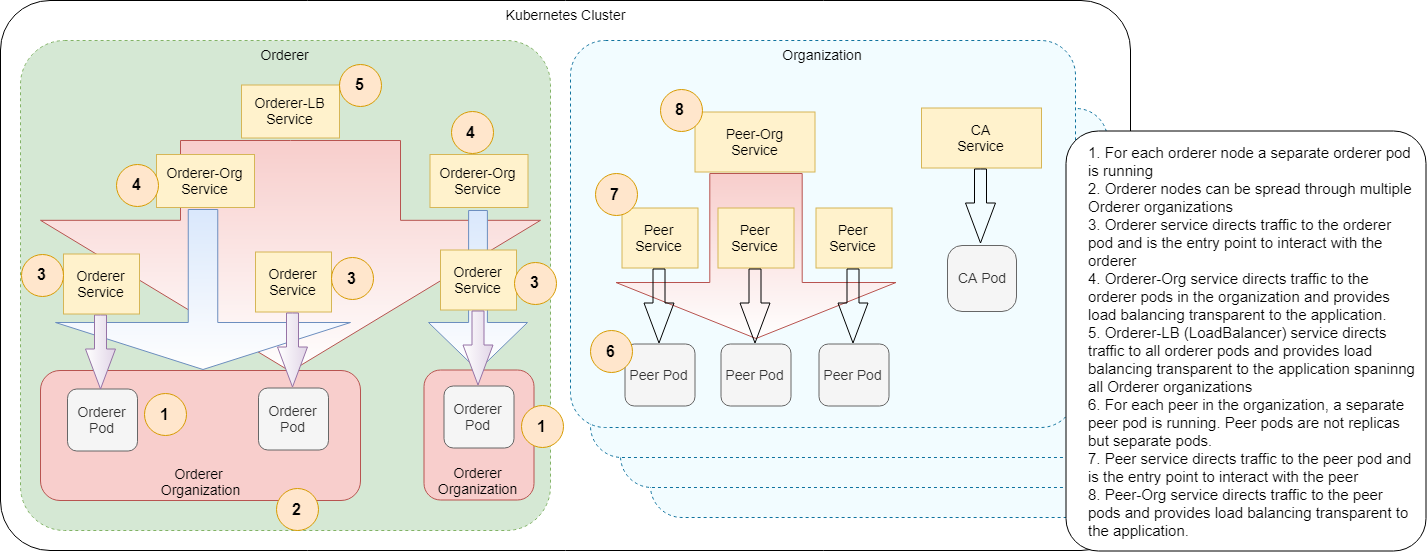
GitHub splunk/hyperledgerfabrick8s Helm charts for running and operating Hyperledger Fabric
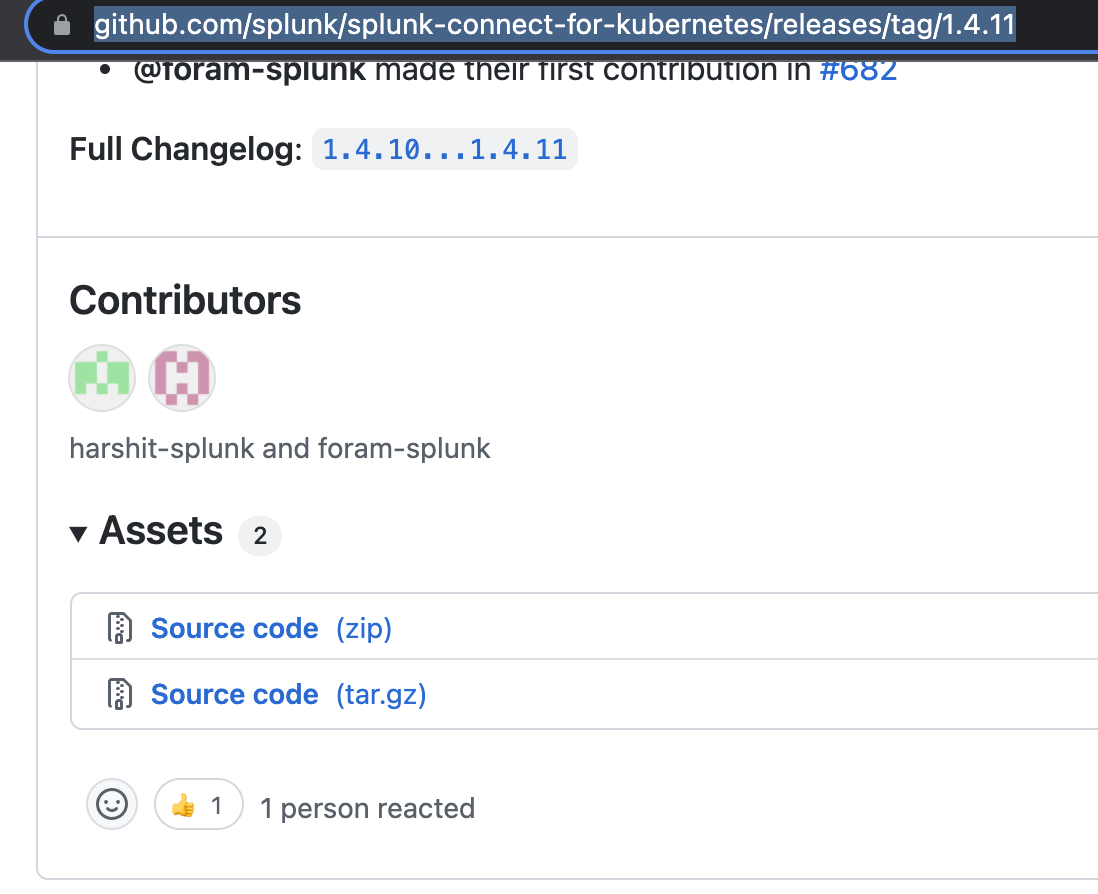
1.4.11 does not have helm chart artifacts · Issue 716 ·
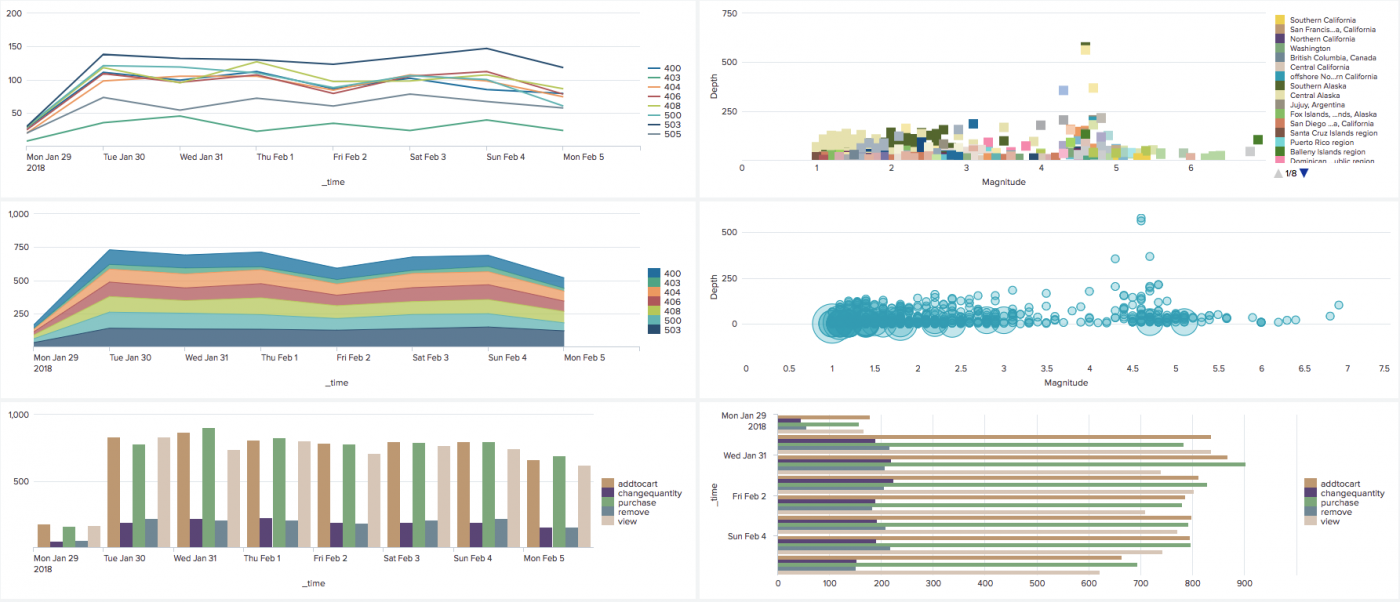
Chart configuration reference Splunk Documentation

Expose concat controls in logging Helm Chart · Issue 315 ·
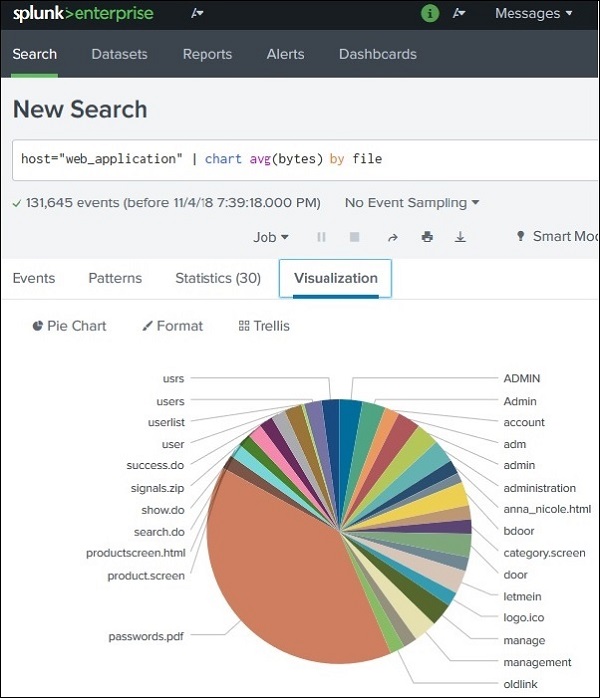
Splunk In Values at Albert Jarman blog
GitHub Helm charts associated with plugins
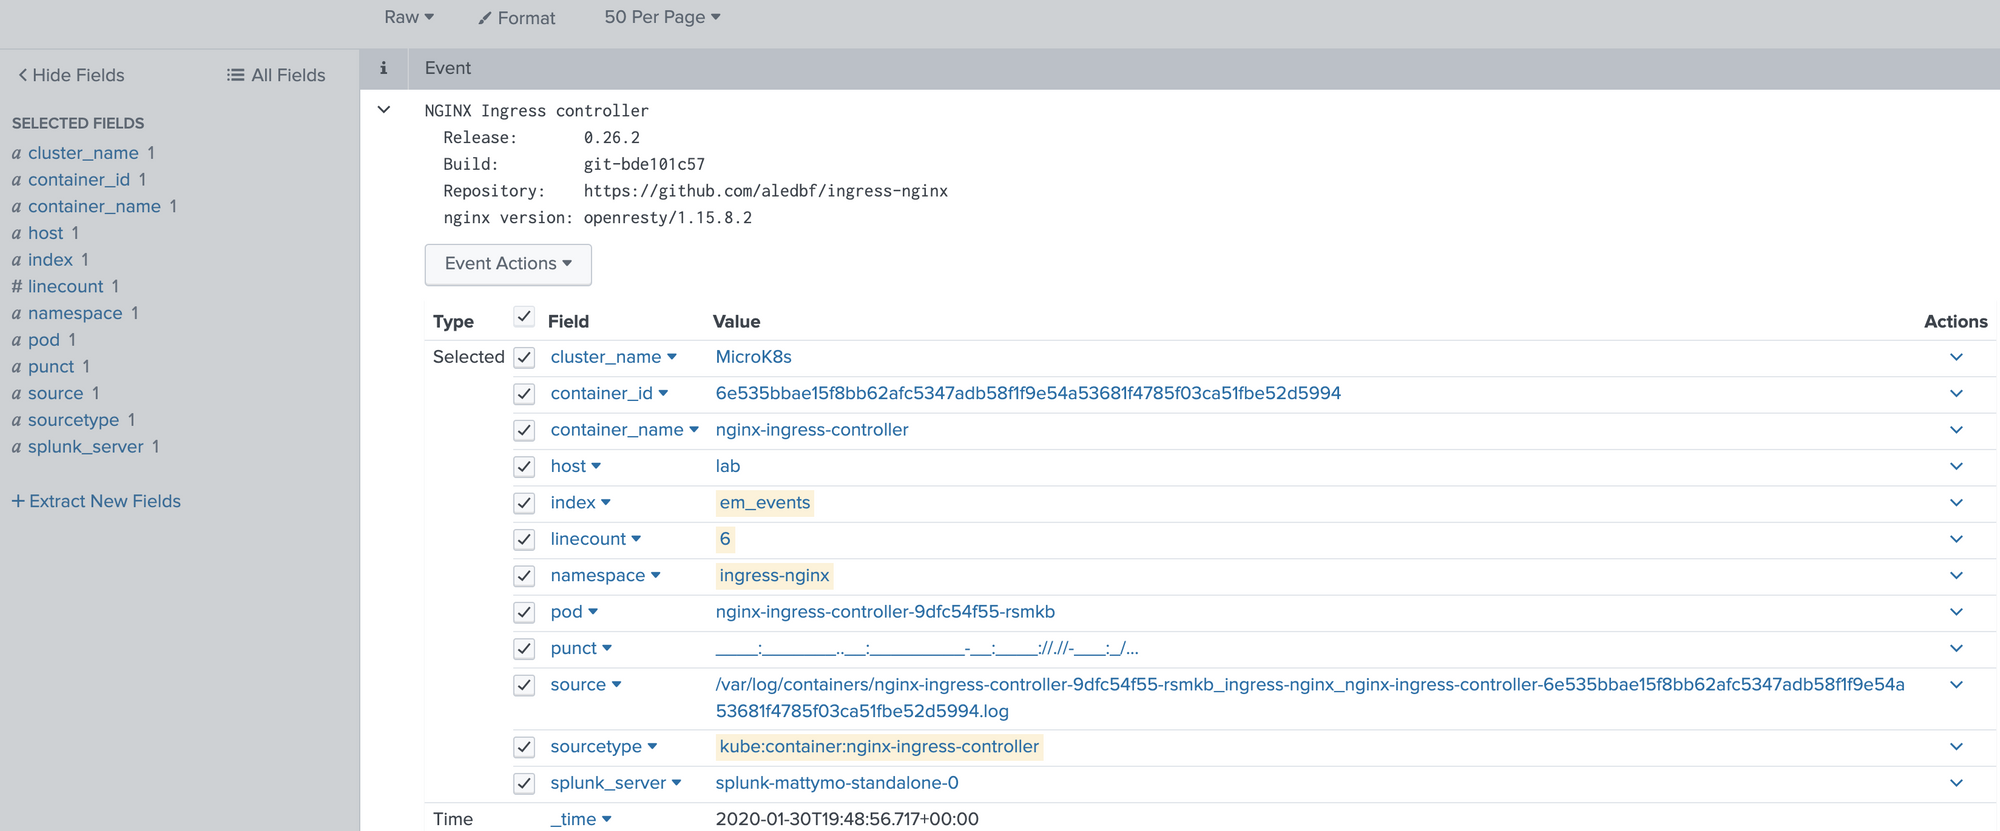
Expose concat controls in logging Helm Chart · Issue 315 ·
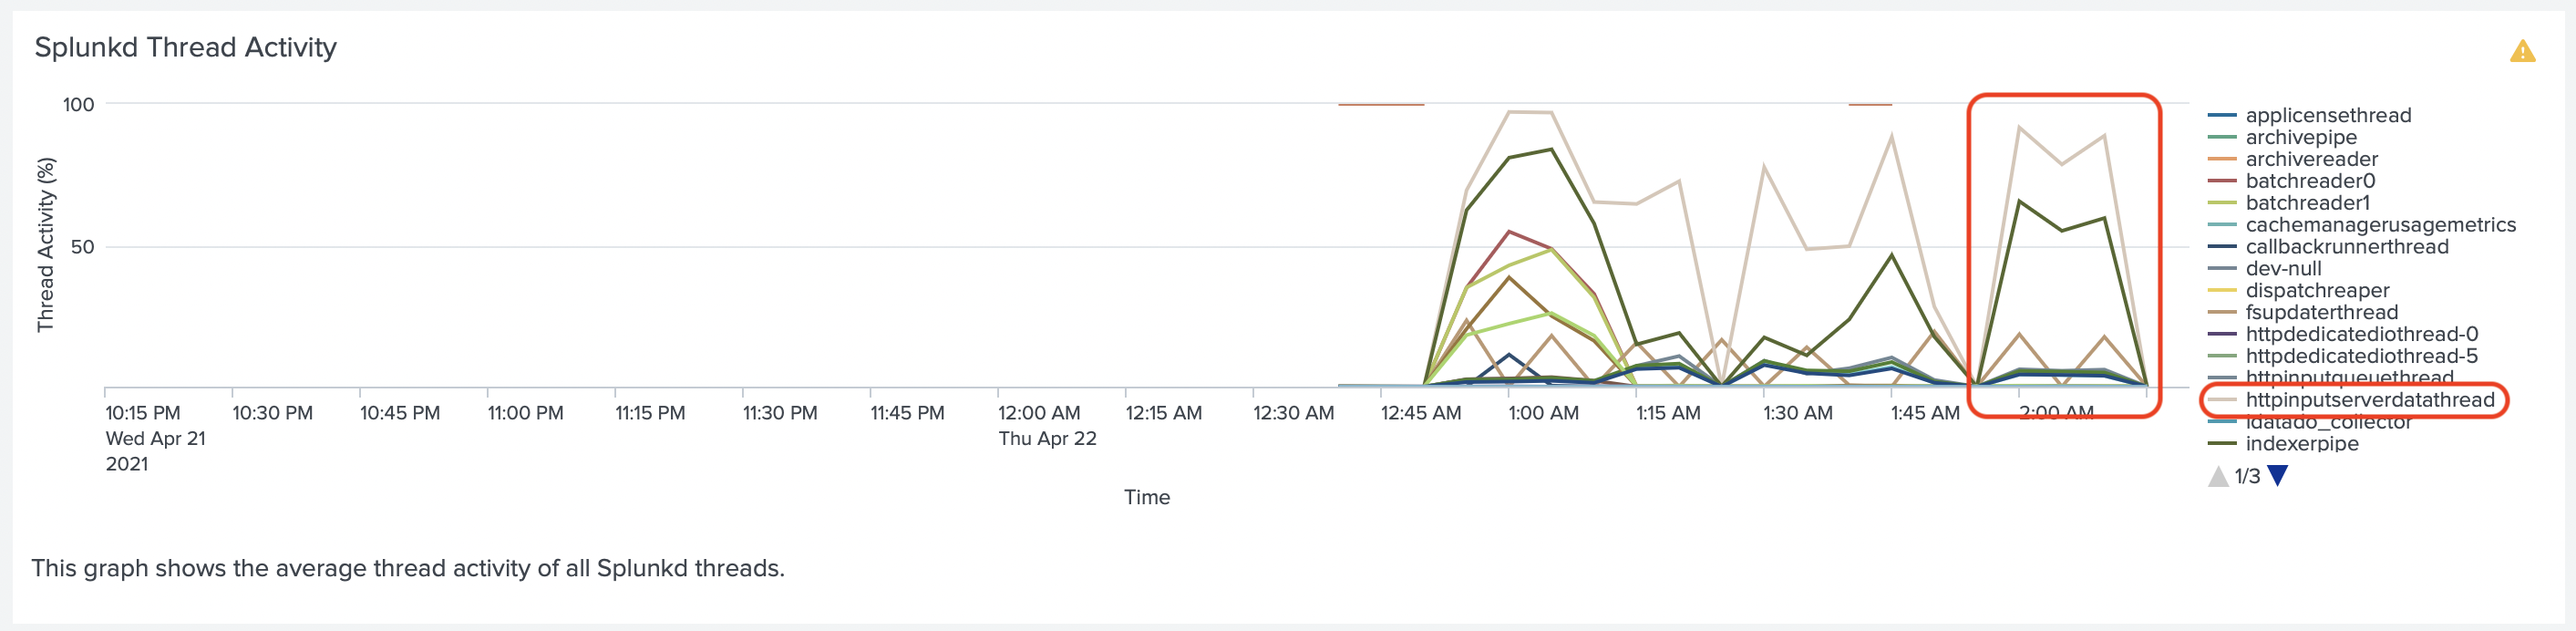
Otel Collector Helm Chart Portal.posgradount.edu.pe
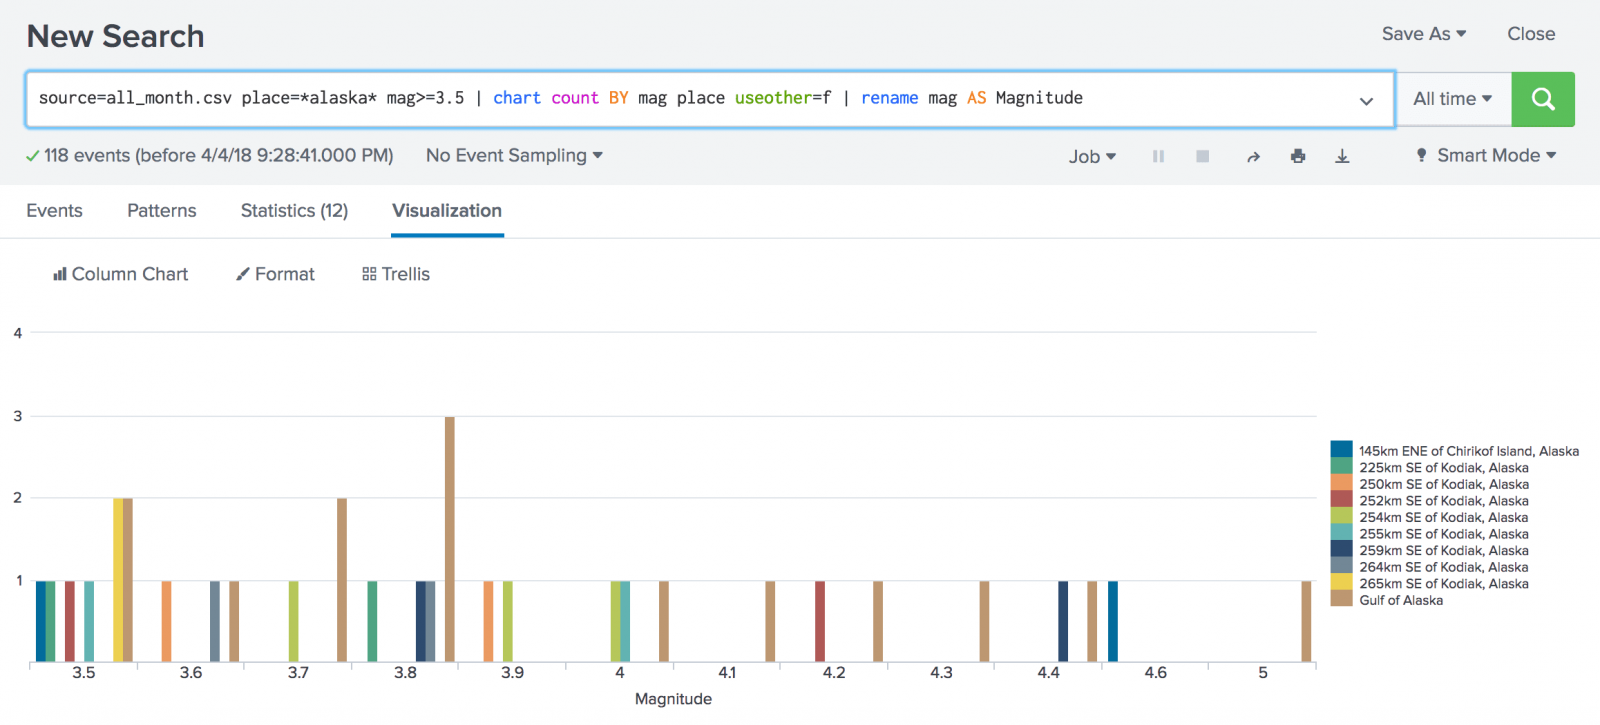
chart Splunk Documentation
Splunk Enterprise And Universal Forwarder Currently Use An Embedded.
Splunk Becomes The Only Vendor To Bring Truly Unified Threat Detection, Investigation, And Response.
We Are Pleased To Announce The General Availability Of Splunk Enterprise Security 8.1.
I Have Another Index That Is.
Related Post: