Kyverno Helm Chart
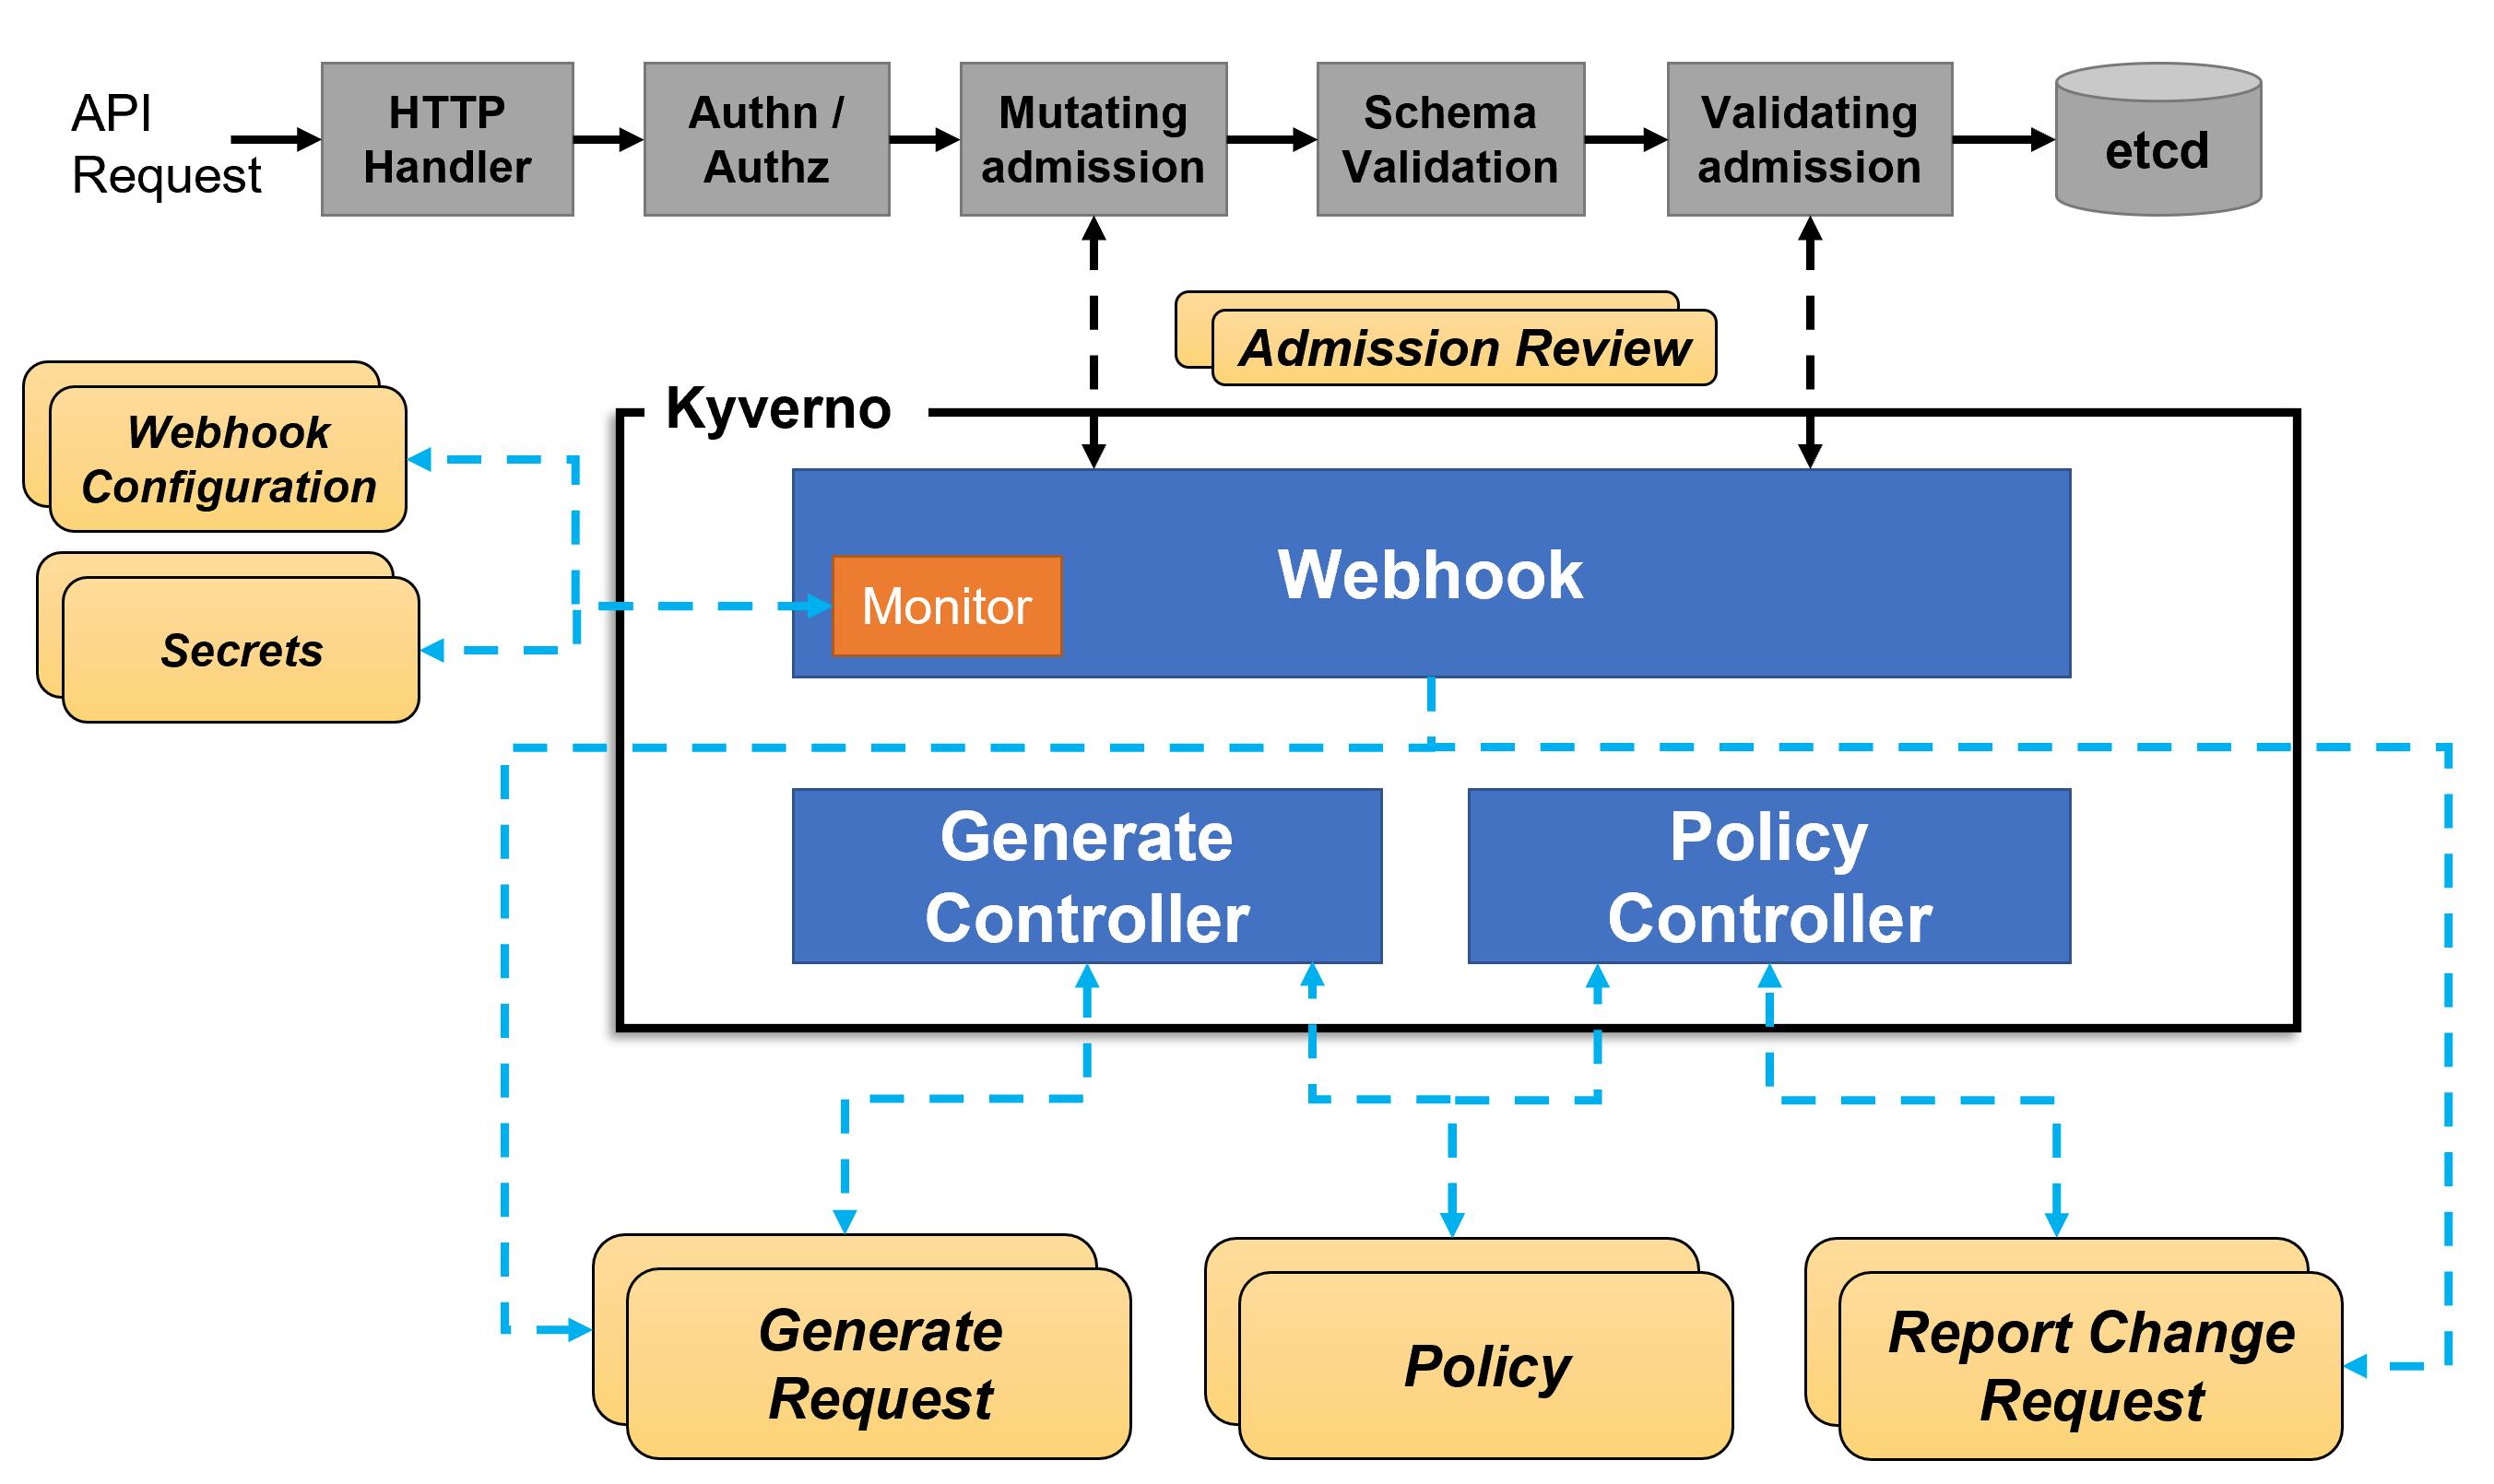
Kyverno Helm Chart - Kyverno policy can help ensure, both in the cluster and in a ci/cd process via the cli, that policyexceptions conform to your design standards. Kyverno 1.14.0 begins a new chapter for kyverno with the introduction of specialized policy types that separate concerns and confusion about validation checks being. Kyverno policies can use the kubernetes api to fetch a resource, or even collections of resource types, for use in a policy. To use in your environment, make sure you test with the right. Additionally, kyverno allows applying jmespath (json match. Kyverno provides multiple methods for installation: Can occur on either validate or mutate policies. Kyverno (greek for “govern”) is a cloud native policy engine. When installing in a production environment, helm is the recommended and most flexible. It was originally built for kubernetes and now can also be used outside of kubernetes clusters as a unified policy. Kyverno provides multiple methods for installation: When installing in a production environment, helm is the recommended and most flexible. High availability understand the various components of kyverno and how it impacts high availability. Kyverno policy can help ensure, both in the cluster and in a ci/cd process via the cli, that policyexceptions conform to your design standards. Kyverno 1.14.0 begins a new chapter for kyverno with the introduction of specialized policy types that separate concerns and confusion about validation checks being. It was originally built for kubernetes and now can also be used outside of kubernetes clusters as a unified policy. Kyverno policies can use the kubernetes api to fetch a resource, or even collections of resource types, for use in a policy. Kyverno (greek for “govern”) is a cloud native policy engine. Additionally, kyverno allows applying jmespath (json match. Kyverno will attempt to validate the schema of a policy and fail if it cannot determine it satisfies the openapi schema definition for that resource. The policies here are maintained by the community and are as samples that demonstrate the power and flexibility of kyverno. It was originally built for kubernetes and now can also be used outside of kubernetes clusters as a unified policy. Kyverno will assist you in these situations by validating and informing you if the admission controller does not have the. Below is an example of a. When installing in a production environment, helm is the recommended and most flexible. Kyverno will assist you in these situations by validating and informing you if the admission controller does not have the level of permissions required at the time the policy is. Can occur on either validate or mutate policies. The policies here. Can occur on either validate or mutate policies. Kyverno 1.14.0 begins a new chapter for kyverno with the introduction of specialized policy types that separate concerns and confusion about validation checks being. Additionally, kyverno allows applying jmespath (json match. To use in your environment, make sure you test with the right. Below is an example of a. It was originally built for kubernetes and now can also be used outside of kubernetes clusters as a unified policy. High availability understand the various components of kyverno and how it impacts high availability. Kyverno provides multiple methods for installation: Can occur on either validate or mutate policies. The policies here are maintained by the community and are as samples. Kyverno provides multiple methods for installation: To use in your environment, make sure you test with the right. Can occur on either validate or mutate policies. When installing in a production environment, helm is the recommended and most flexible. Kyverno 1.14.0 begins a new chapter for kyverno with the introduction of specialized policy types that separate concerns and confusion about. Kyverno will assist you in these situations by validating and informing you if the admission controller does not have the level of permissions required at the time the policy is. Kyverno provides multiple methods for installation: The policies here are maintained by the community and are as samples that demonstrate the power and flexibility of kyverno. Kyverno (greek for “govern”). High availability understand the various components of kyverno and how it impacts high availability. Kyverno will assist you in these situations by validating and informing you if the admission controller does not have the level of permissions required at the time the policy is. Kyverno policies can use the kubernetes api to fetch a resource, or even collections of resource. Below is an example of a. Kyverno will assist you in these situations by validating and informing you if the admission controller does not have the level of permissions required at the time the policy is. High availability understand the various components of kyverno and how it impacts high availability. Can occur on either validate or mutate policies. It was. High availability understand the various components of kyverno and how it impacts high availability. When installing in a production environment, helm is the recommended and most flexible. Kyverno will assist you in these situations by validating and informing you if the admission controller does not have the level of permissions required at the time the policy is. Kyverno will attempt. Kyverno policy can help ensure, both in the cluster and in a ci/cd process via the cli, that policyexceptions conform to your design standards. High availability understand the various components of kyverno and how it impacts high availability. Kyverno will assist you in these situations by validating and informing you if the admission controller does not have the level of. Kyverno (greek for “govern”) is a cloud native policy engine. When installing in a production environment, helm is the recommended and most flexible. Kyverno will attempt to validate the schema of a policy and fail if it cannot determine it satisfies the openapi schema definition for that resource. The policies here are maintained by the community and are as samples that demonstrate the power and flexibility of kyverno. Additionally, kyverno allows applying jmespath (json match. Kyverno policy can help ensure, both in the cluster and in a ci/cd process via the cli, that policyexceptions conform to your design standards. To use in your environment, make sure you test with the right. Kyverno provides multiple methods for installation: Below is an example of a. Kyverno policies can use the kubernetes api to fetch a resource, or even collections of resource types, for use in a policy. Kyverno 1.14.0 begins a new chapter for kyverno with the introduction of specialized policy types that separate concerns and confusion about validation checks being. Can occur on either validate or mutate policies.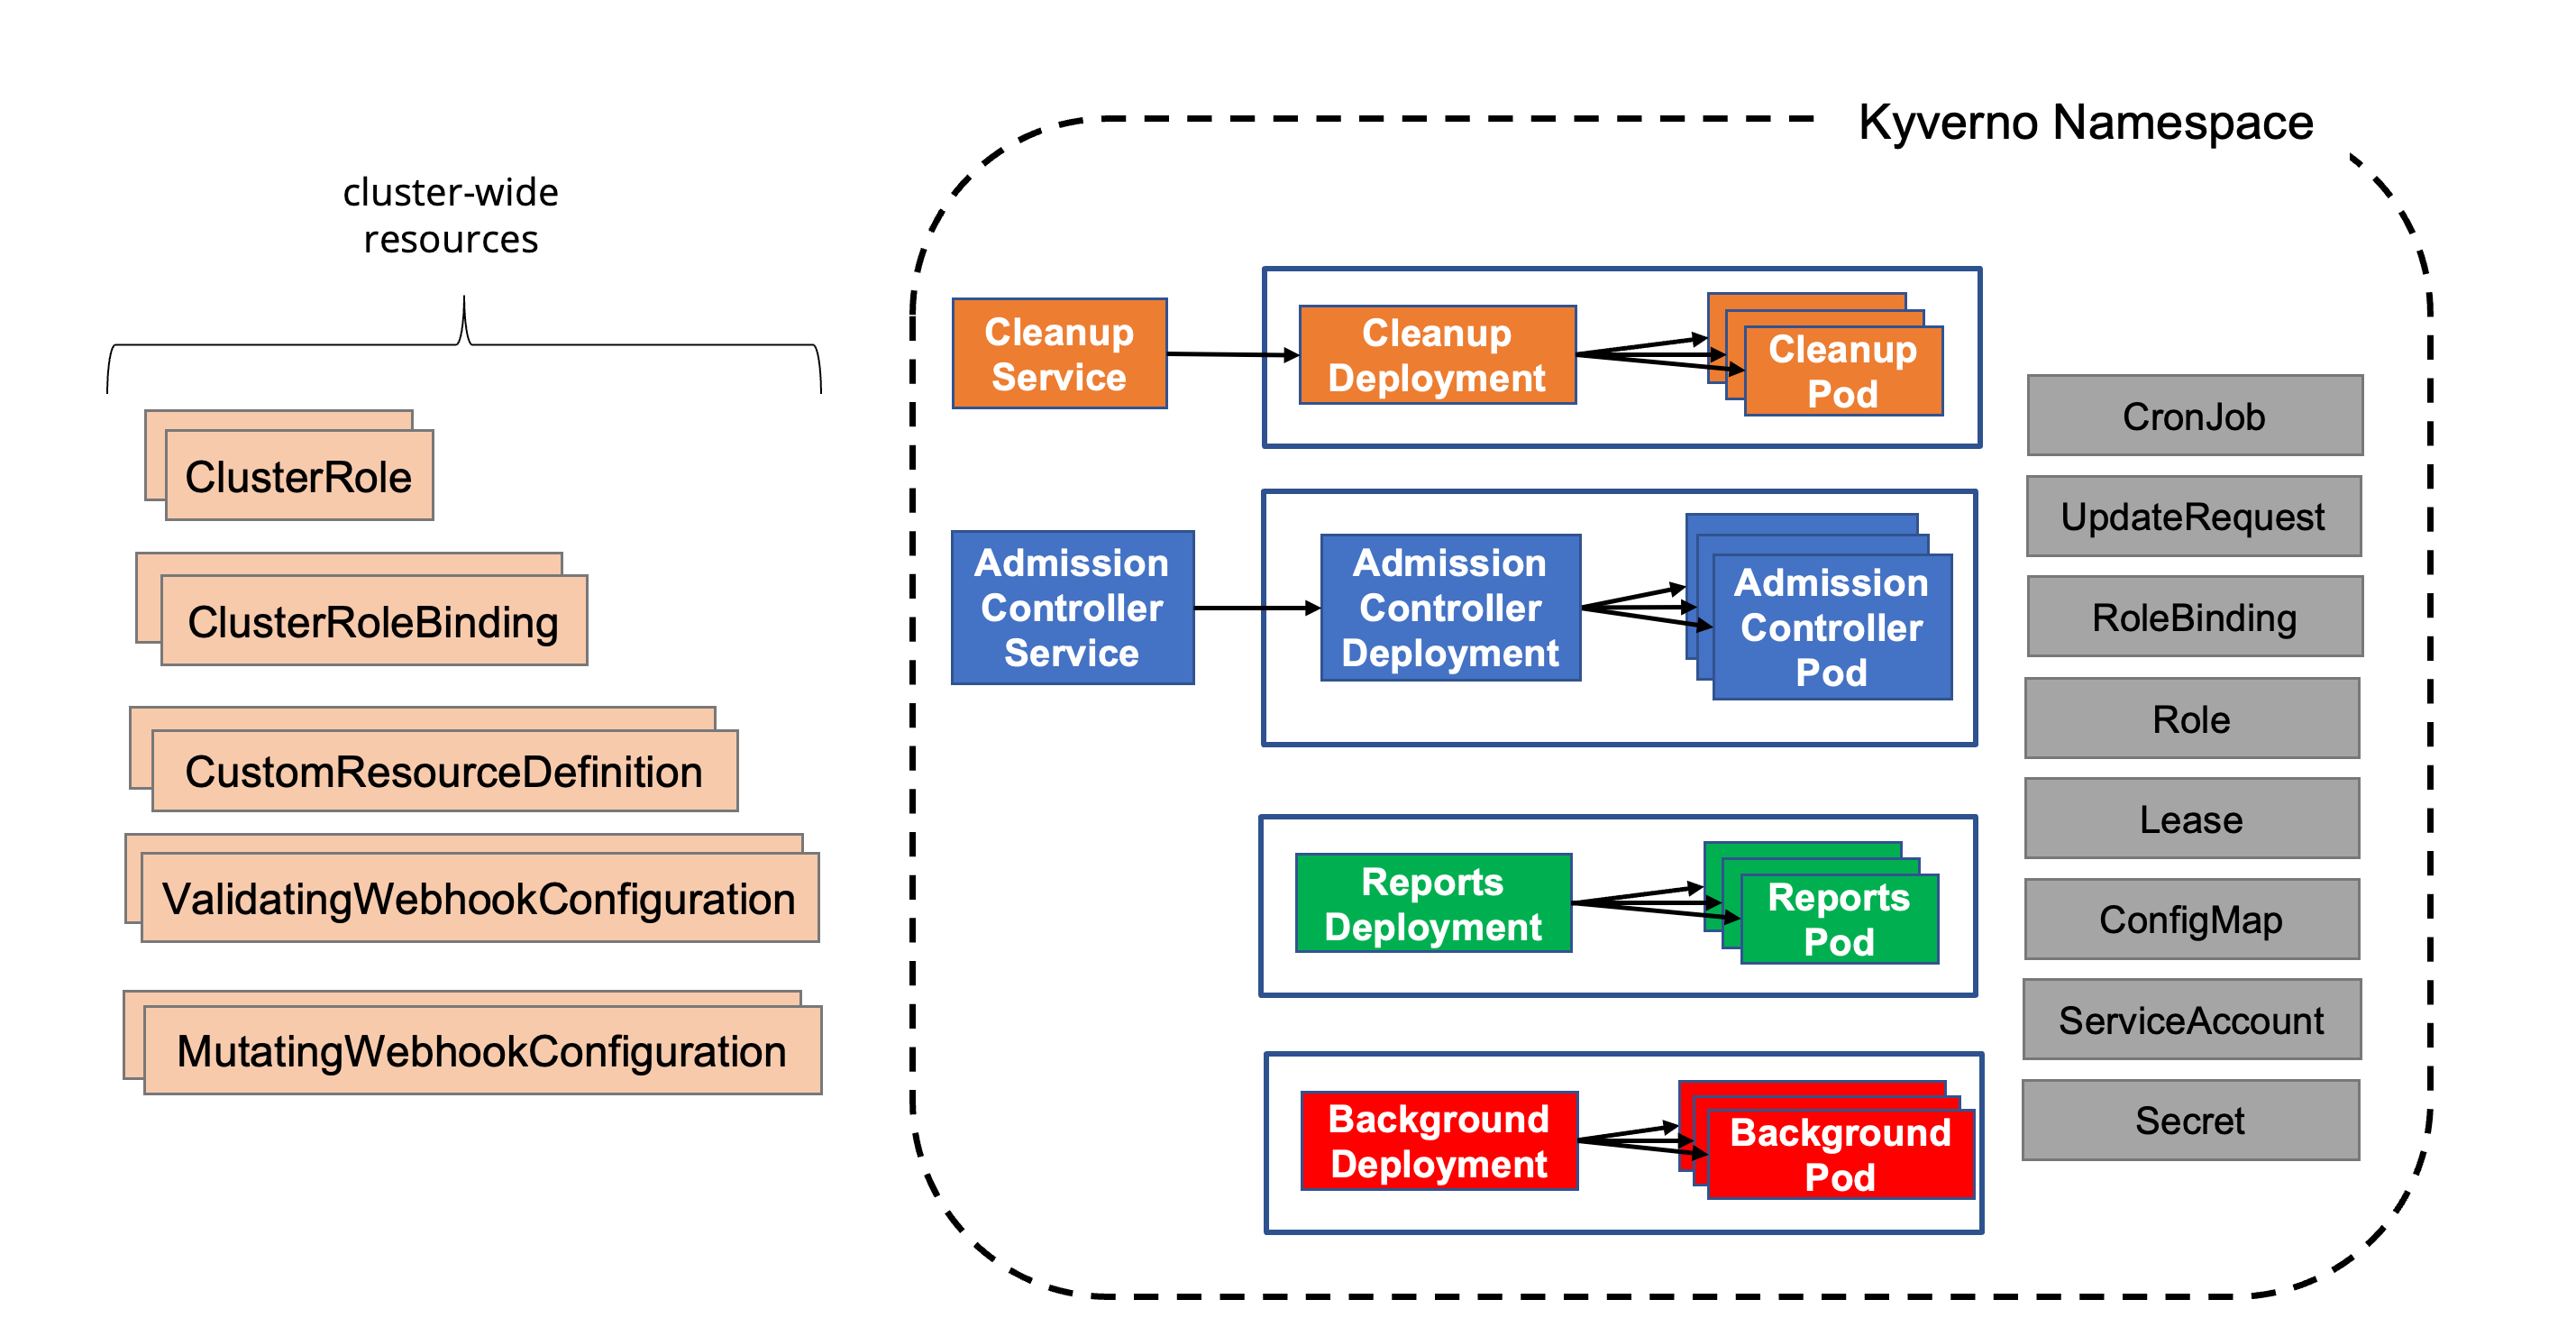
Installation Kyverno
Kyverno native policy management for k8s admins
GitHub nirmata/kyvernocharts Repository for Nirmata supported Helm charts for Kyverno
Installing Kyverno Policies in Cluster using Helm Charts Error and Solution
[BUG] Helm chart installation fails due to PDB api version on k8s

GitHub iamraj007/helmcharts kyverno policies (Cluster level) for AKS the basic custom ones

[OFFICIAL] Kyverno Helm Chart · Issue 2929 · artifacthub/hub · GitHub
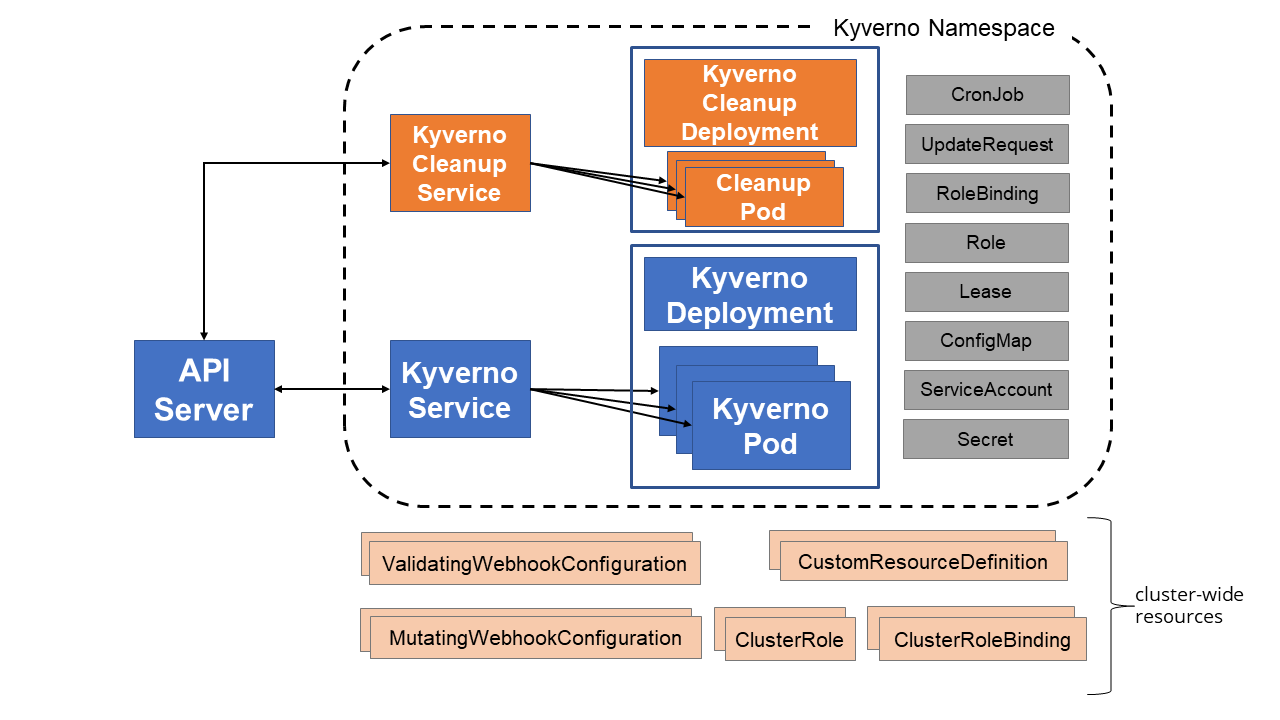
Installation Kyverno
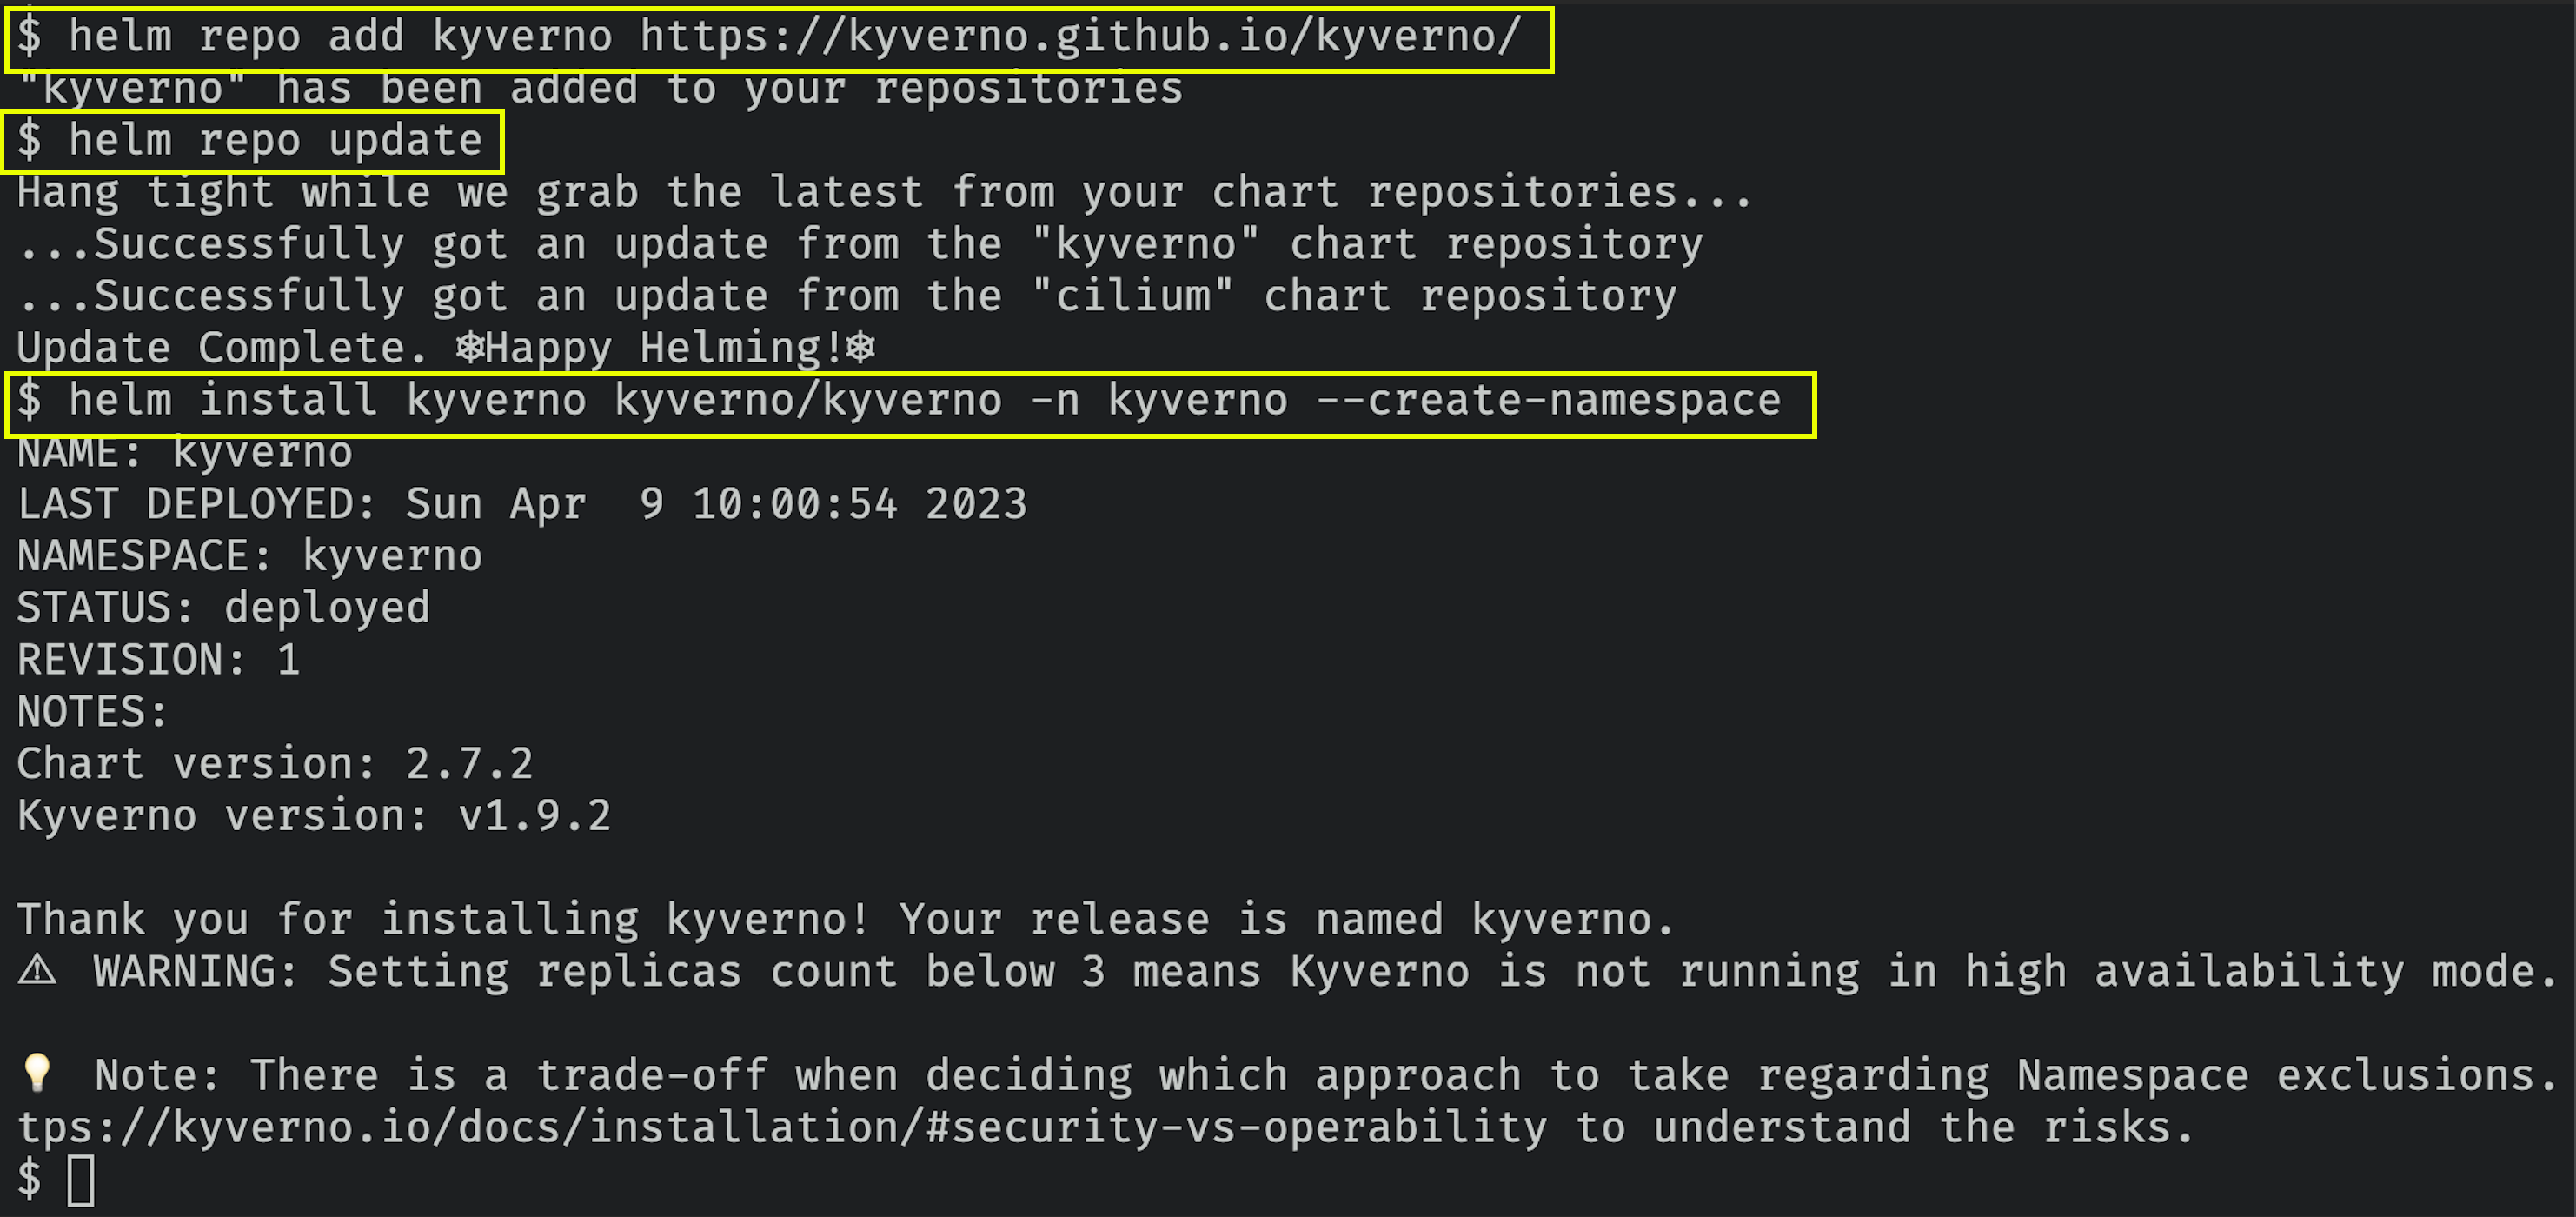
Securing Clusters using Kyverno Policy Engine Goat
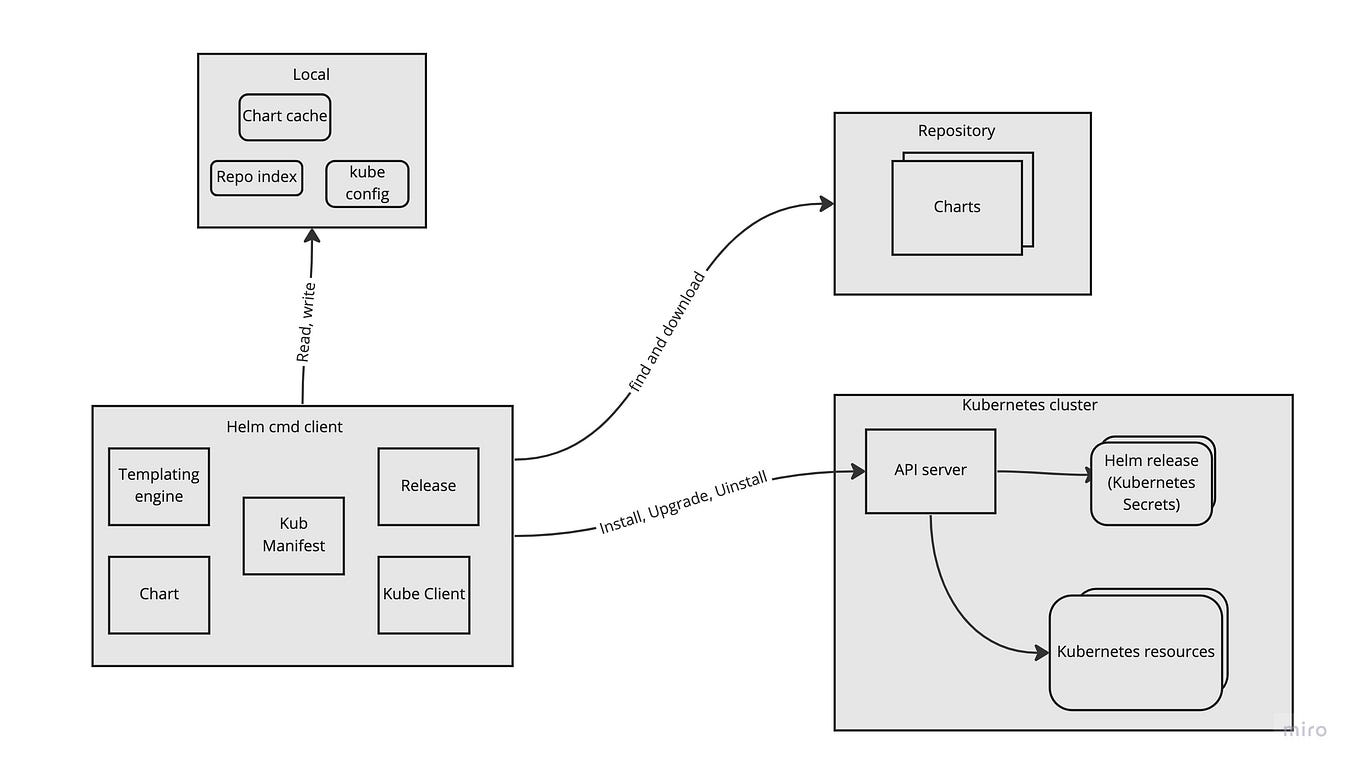
Kyverno A Native Policy Management by Anoop Ka Groww Engineering
High Availability Understand The Various Components Of Kyverno And How It Impacts High Availability.
It Was Originally Built For Kubernetes And Now Can Also Be Used Outside Of Kubernetes Clusters As A Unified Policy.
Kyverno Will Assist You In These Situations By Validating And Informing You If The Admission Controller Does Not Have The Level Of Permissions Required At The Time The Policy Is.
Related Post: