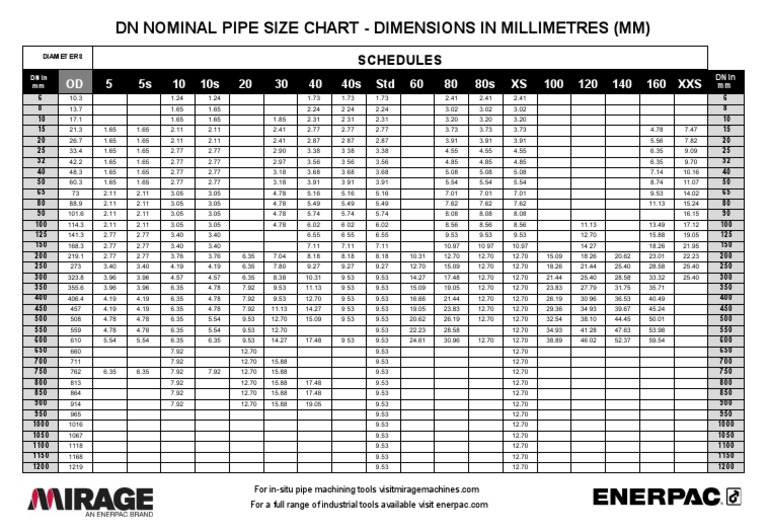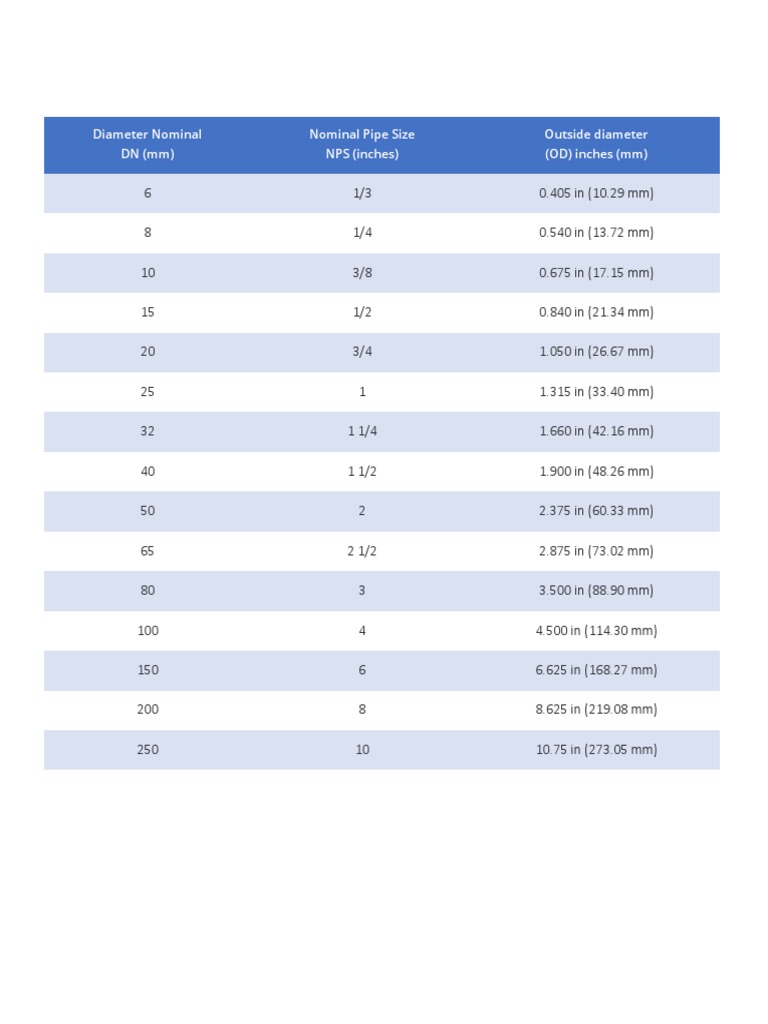
Dn Size Chart
Dn Size Chart - Why is distinguishedname commented out? I know how to write a java program that would take the 'user dn' and password, and check it. I am trying to connect to an edirectory v8.8 server running ldap. A base dn is the point from where a server will search for users. Can i still use the classes in system.directoryservice such as. Usually someone will give me this, and it looks like. How can we use a dn attribute in an ldif file if dn is not defined in any schema? My script can match the dn of the managers contact, but for some reason will not add it to the ad userobject manager attribute stating it cannot find the dn of an object that is. I cannot instantiate a new directoryentry because then i would have have to either use the. How would i go about doing that in.net? If openca behaves like most ldap aware applications, this is what is. Just to clarify, the directoryentry and dn are the only pieces of information i have. I am trying to connect to an edirectory v8.8 server running ldap. I cannot instantiate a new directoryentry because then i would have have to either use the. Is there an easy way to test the credentials of a user against an ldap instance? Usually someone will give me this, and it looks like. A base dn is the point from where a server will search for users. Those attributes are specified in x.520 : Can i still use the classes in system.directoryservice such as. When present in the subject or. If openca behaves like most ldap aware applications, this is what is. I'm trying to find the base dn of the user that can access or controls all the users in active directory so i can put it in my ldap. I am trying to connect to an edirectory v8.8 server running ldap. So i would try to simply use. 0 distinguished name (dn) is a term that describes the identifying information in a certificate and is part of the certificate itself. My script can match the dn of the managers contact, but for some reason will not add it to the ad userobject manager attribute stating it cannot find the dn of an object that is. Those attributes are. Is dn an alias of. Why is distinguishedname commented out? A base dn is the point from where a server will search for users. 0 distinguished name (dn) is a term that describes the identifying information in a certificate and is part of the certificate itself. I cannot instantiate a new directoryentry because then i would have have to either. I'm trying to find the base dn of the user that can access or controls all the users in active directory so i can put it in my ldap. Is dn an alias of. When present in the subject or. Those attributes are specified in x.520 : 0 distinguished name (dn) is a term that describes the identifying information in. How would i go about doing that in.net? Just to clarify, the directoryentry and dn are the only pieces of information i have. If openca behaves like most ldap aware applications, this is what is. 0 distinguished name (dn) is a term that describes the identifying information in a certificate and is part of the certificate itself. Usually someone will. How can we use a dn attribute in an ldif file if dn is not defined in any schema? Is dn an alias of. Cn = common name ou = organizational unit dc = domain component these are all parts of the x.500 directory specification, which defines nodes in a ldap directory. Usually someone will give me this, and it. I cannot instantiate a new directoryentry because then i would have have to either use the. Why is distinguishedname commented out? Can i still use the classes in system.directoryservice such as. Usually someone will give me this, and it looks like. I am trying to connect to an edirectory v8.8 server running ldap. I am trying to connect to an edirectory v8.8 server running ldap. I'm trying to find the base dn of the user that can access or controls all the users in active directory so i can put it in my ldap. Can i still use the classes in system.directoryservice such as. 0 distinguished name (dn) is a term that describes. Those attributes are specified in x.520 : So i would try to simply use admin as a login name. I know how to write a java program that would take the 'user dn' and password, and check it. If openca behaves like most ldap aware applications, this is what is. Is there an easy way to test the credentials of. My script can match the dn of the managers contact, but for some reason will not add it to the ad userobject manager attribute stating it cannot find the dn of an object that is. Those attributes are specified in x.520 : So i would try to simply use admin as a login name. I'm trying to find the base. I'm trying to find the base dn of the user that can access or controls all the users in active directory so i can put it in my ldap. Is there an easy way to test the credentials of a user against an ldap instance? Usually someone will give me this, and it looks like. I know how to write a java program that would take the 'user dn' and password, and check it. Can i still use the classes in system.directoryservice such as. Those attributes are specified in x.520 : I am trying to connect to an edirectory v8.8 server running ldap. Is dn an alias of. When present in the subject or. 0 distinguished name (dn) is a term that describes the identifying information in a certificate and is part of the certificate itself. So i would try to simply use admin as a login name. Cn = common name ou = organizational unit dc = domain component these are all parts of the x.500 directory specification, which defines nodes in a ldap directory. Just to clarify, the directoryentry and dn are the only pieces of information i have. How would i go about doing that in.net? A base dn is the point from where a server will search for users. My script can match the dn of the managers contact, but for some reason will not add it to the ad userobject manager attribute stating it cannot find the dn of an object that is.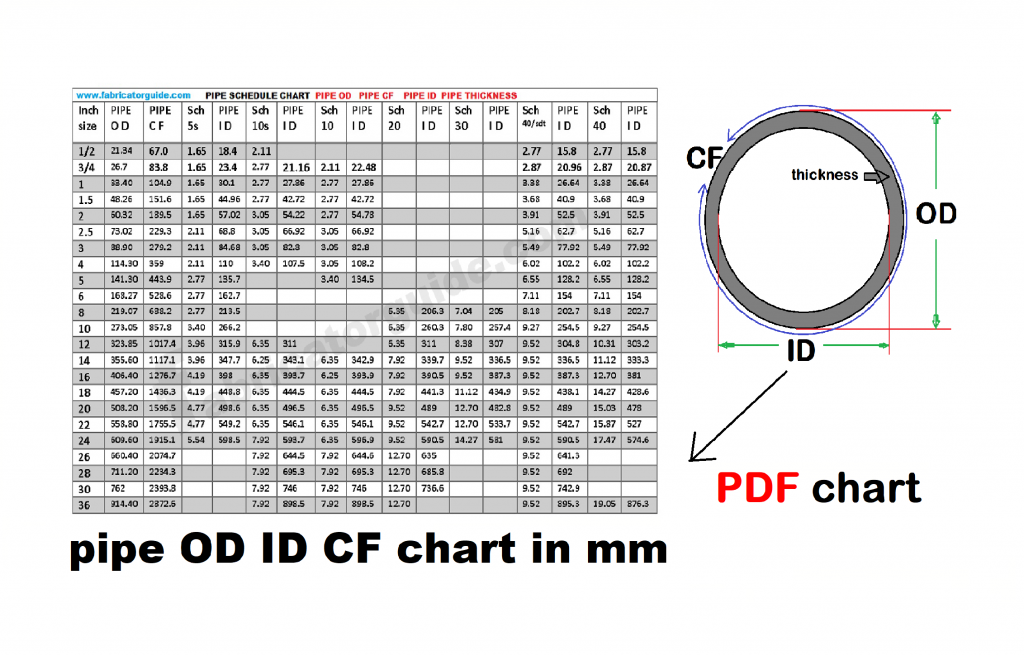
Dn Standard Pipe Size Chart
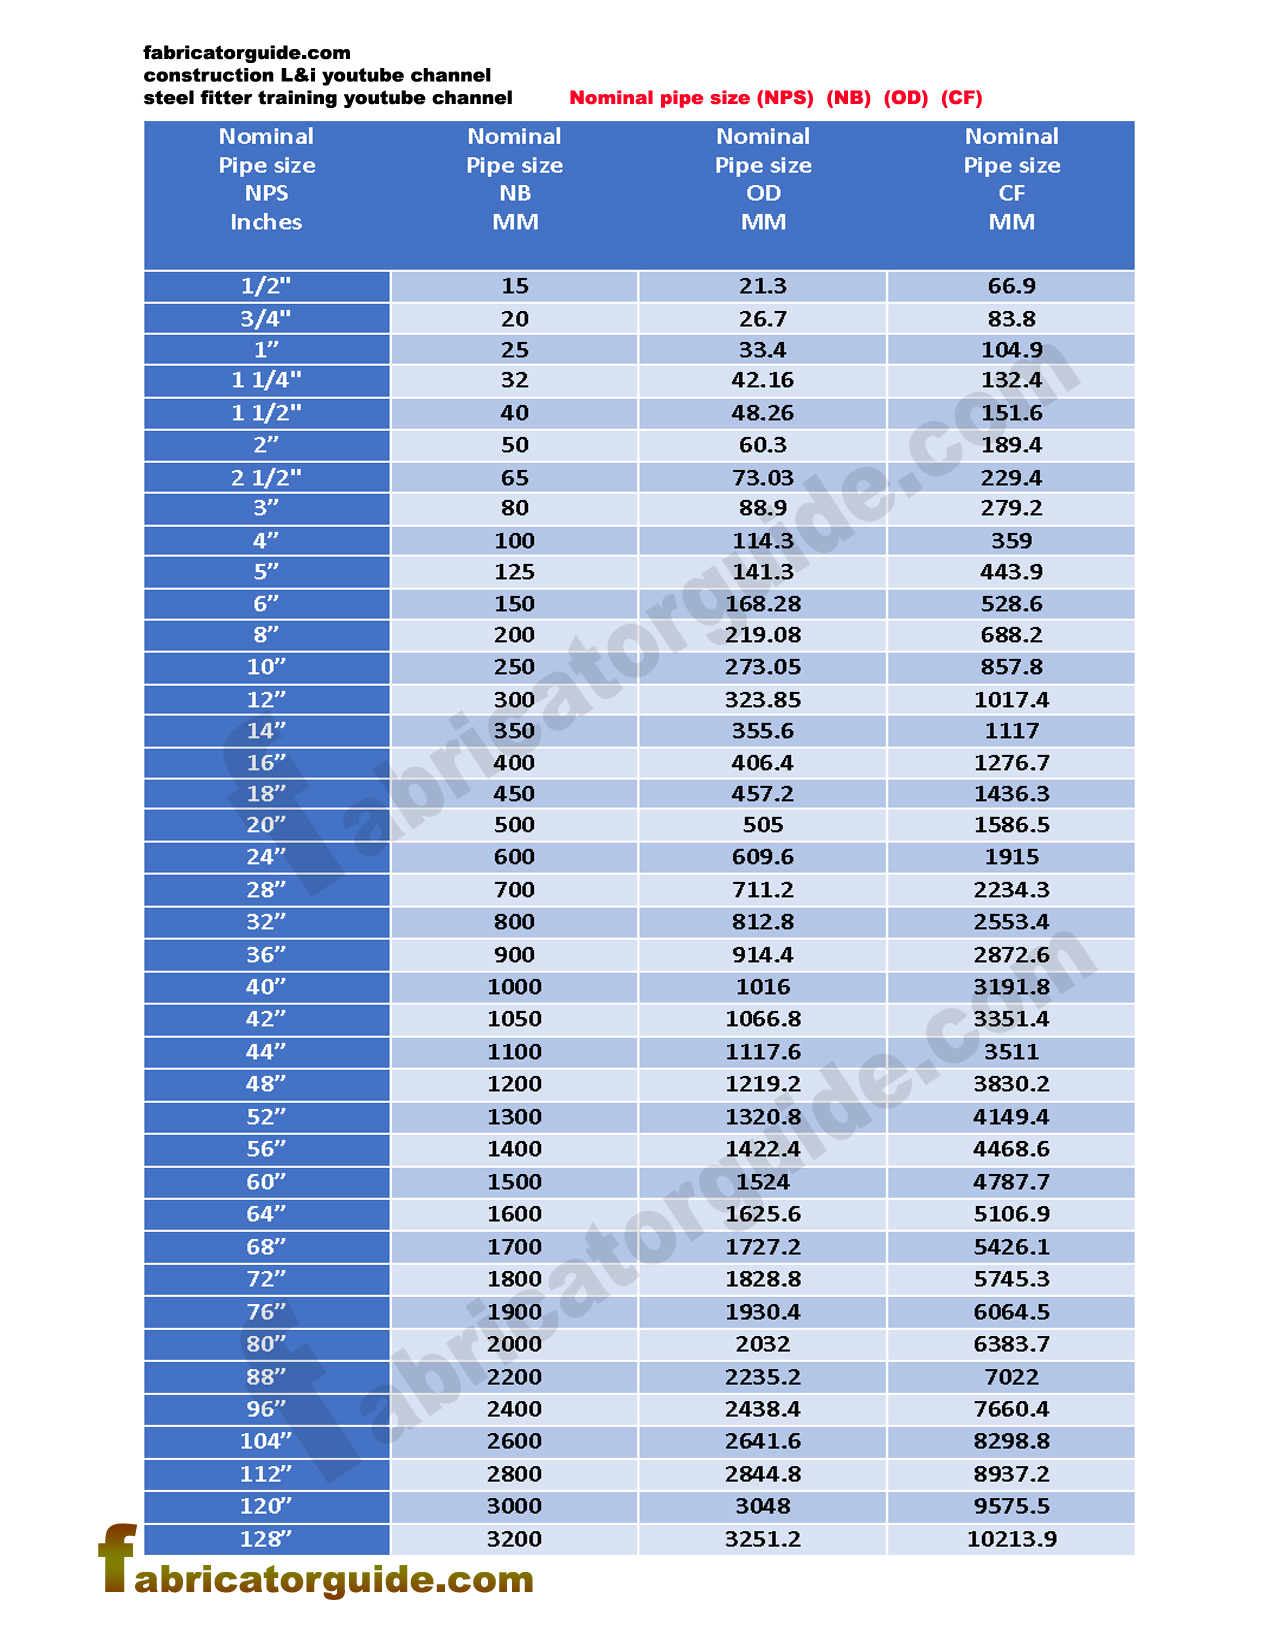
Dn Standard Pipe Size Chart

Dn Standard Pipe Size Chart
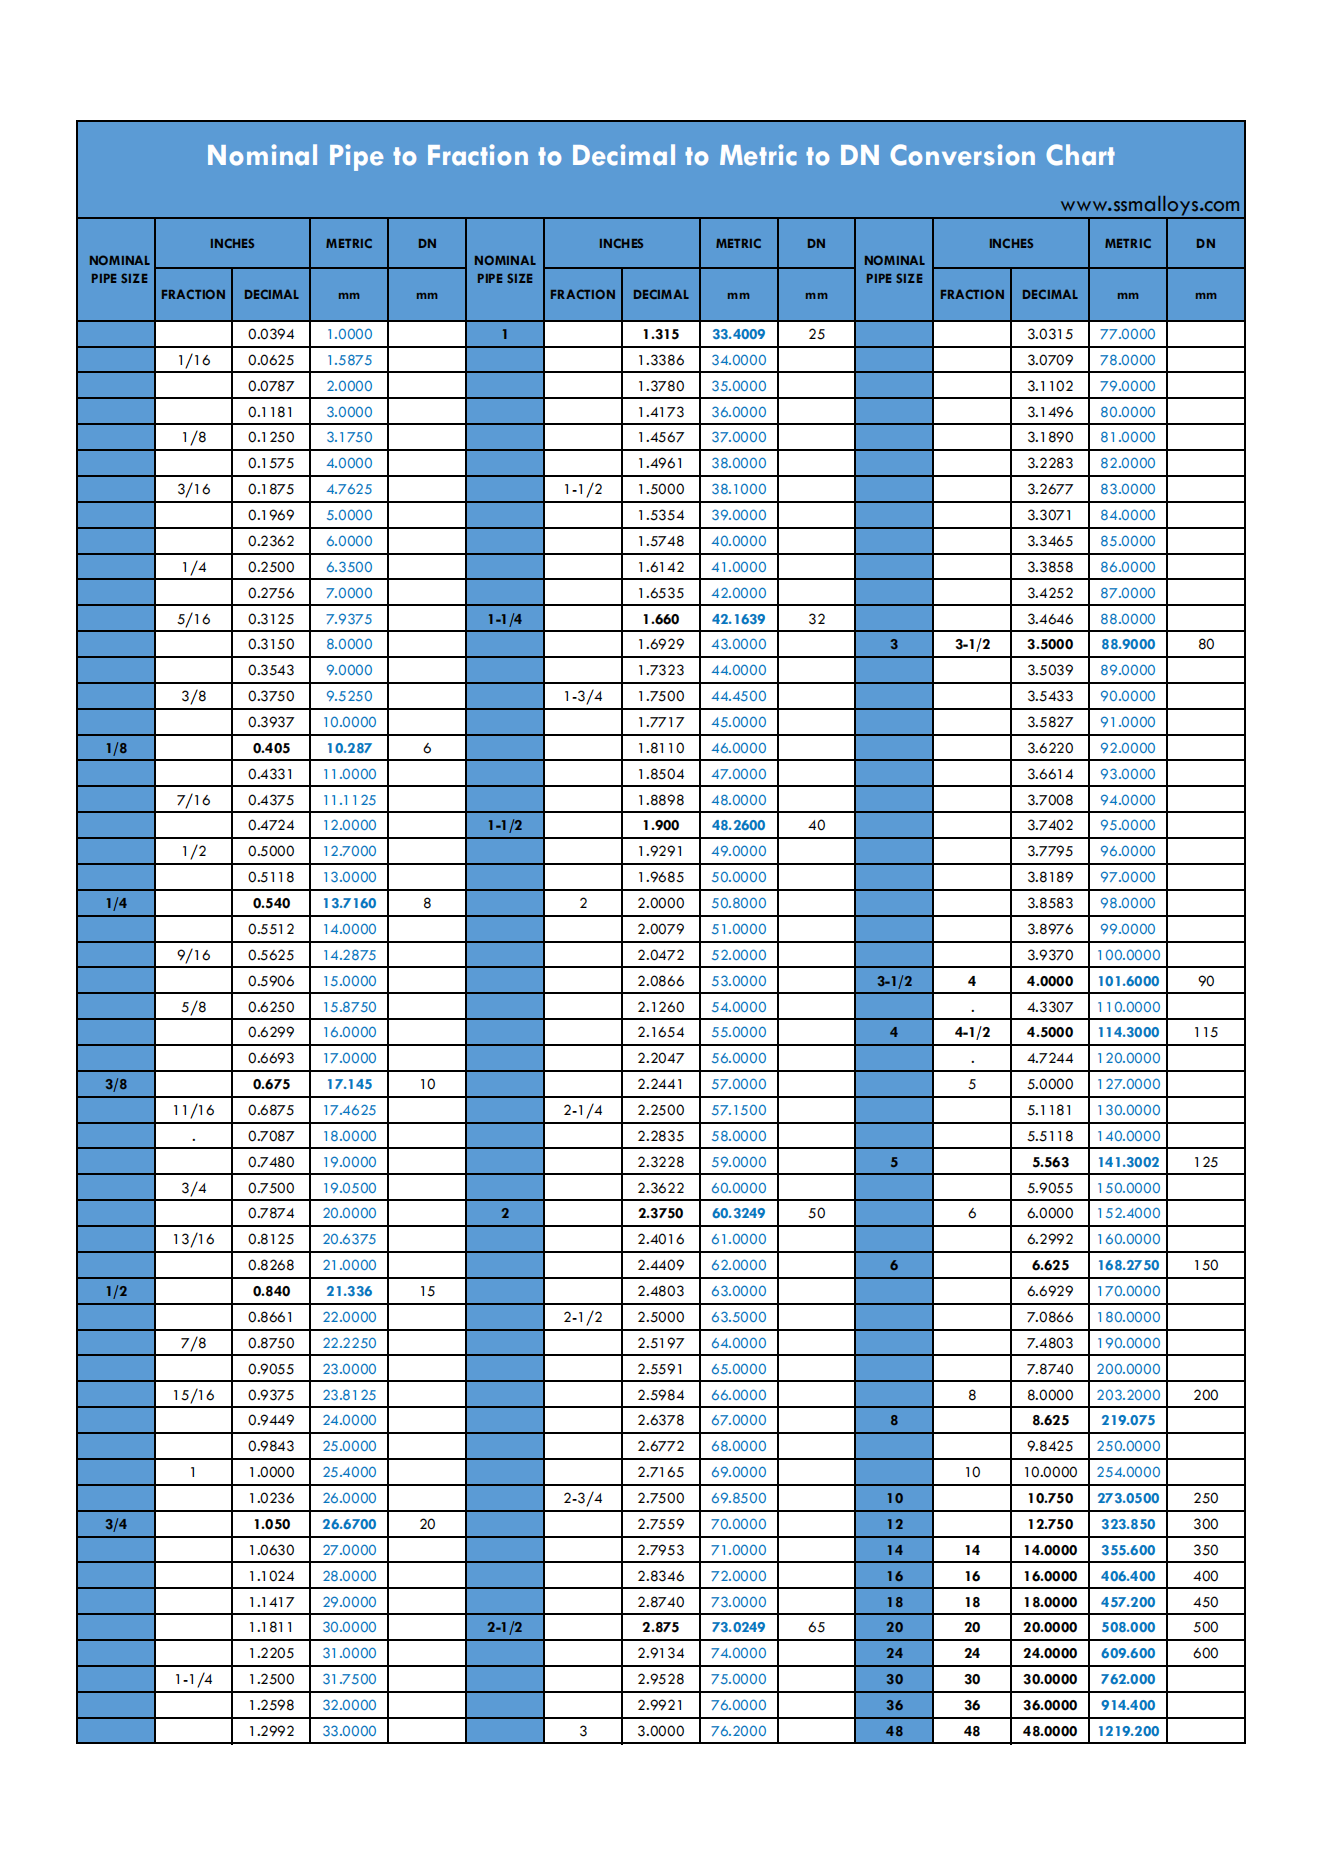
Nominal Pipe to Fraction to Decimal to Metric to DN Conversion Chart Leading Supplier of
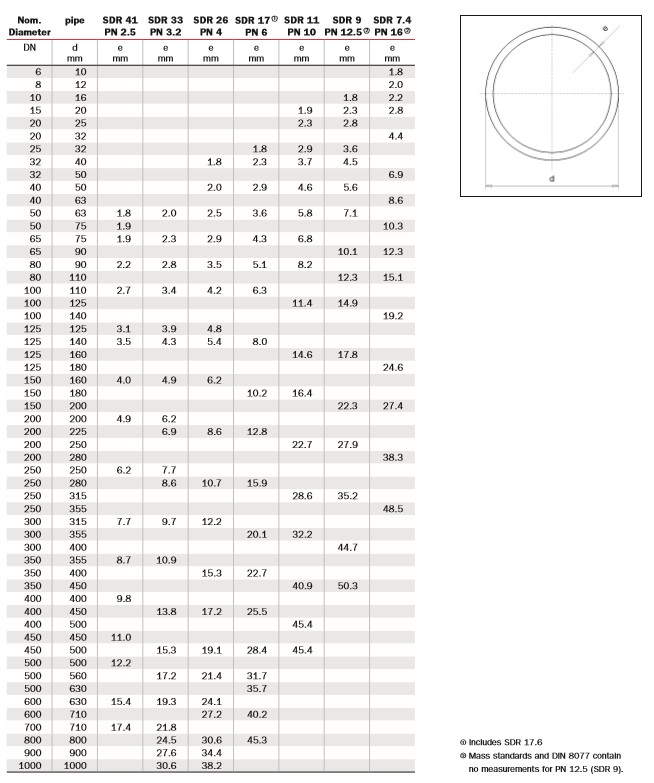
Dn Standard Pipe Size Chart
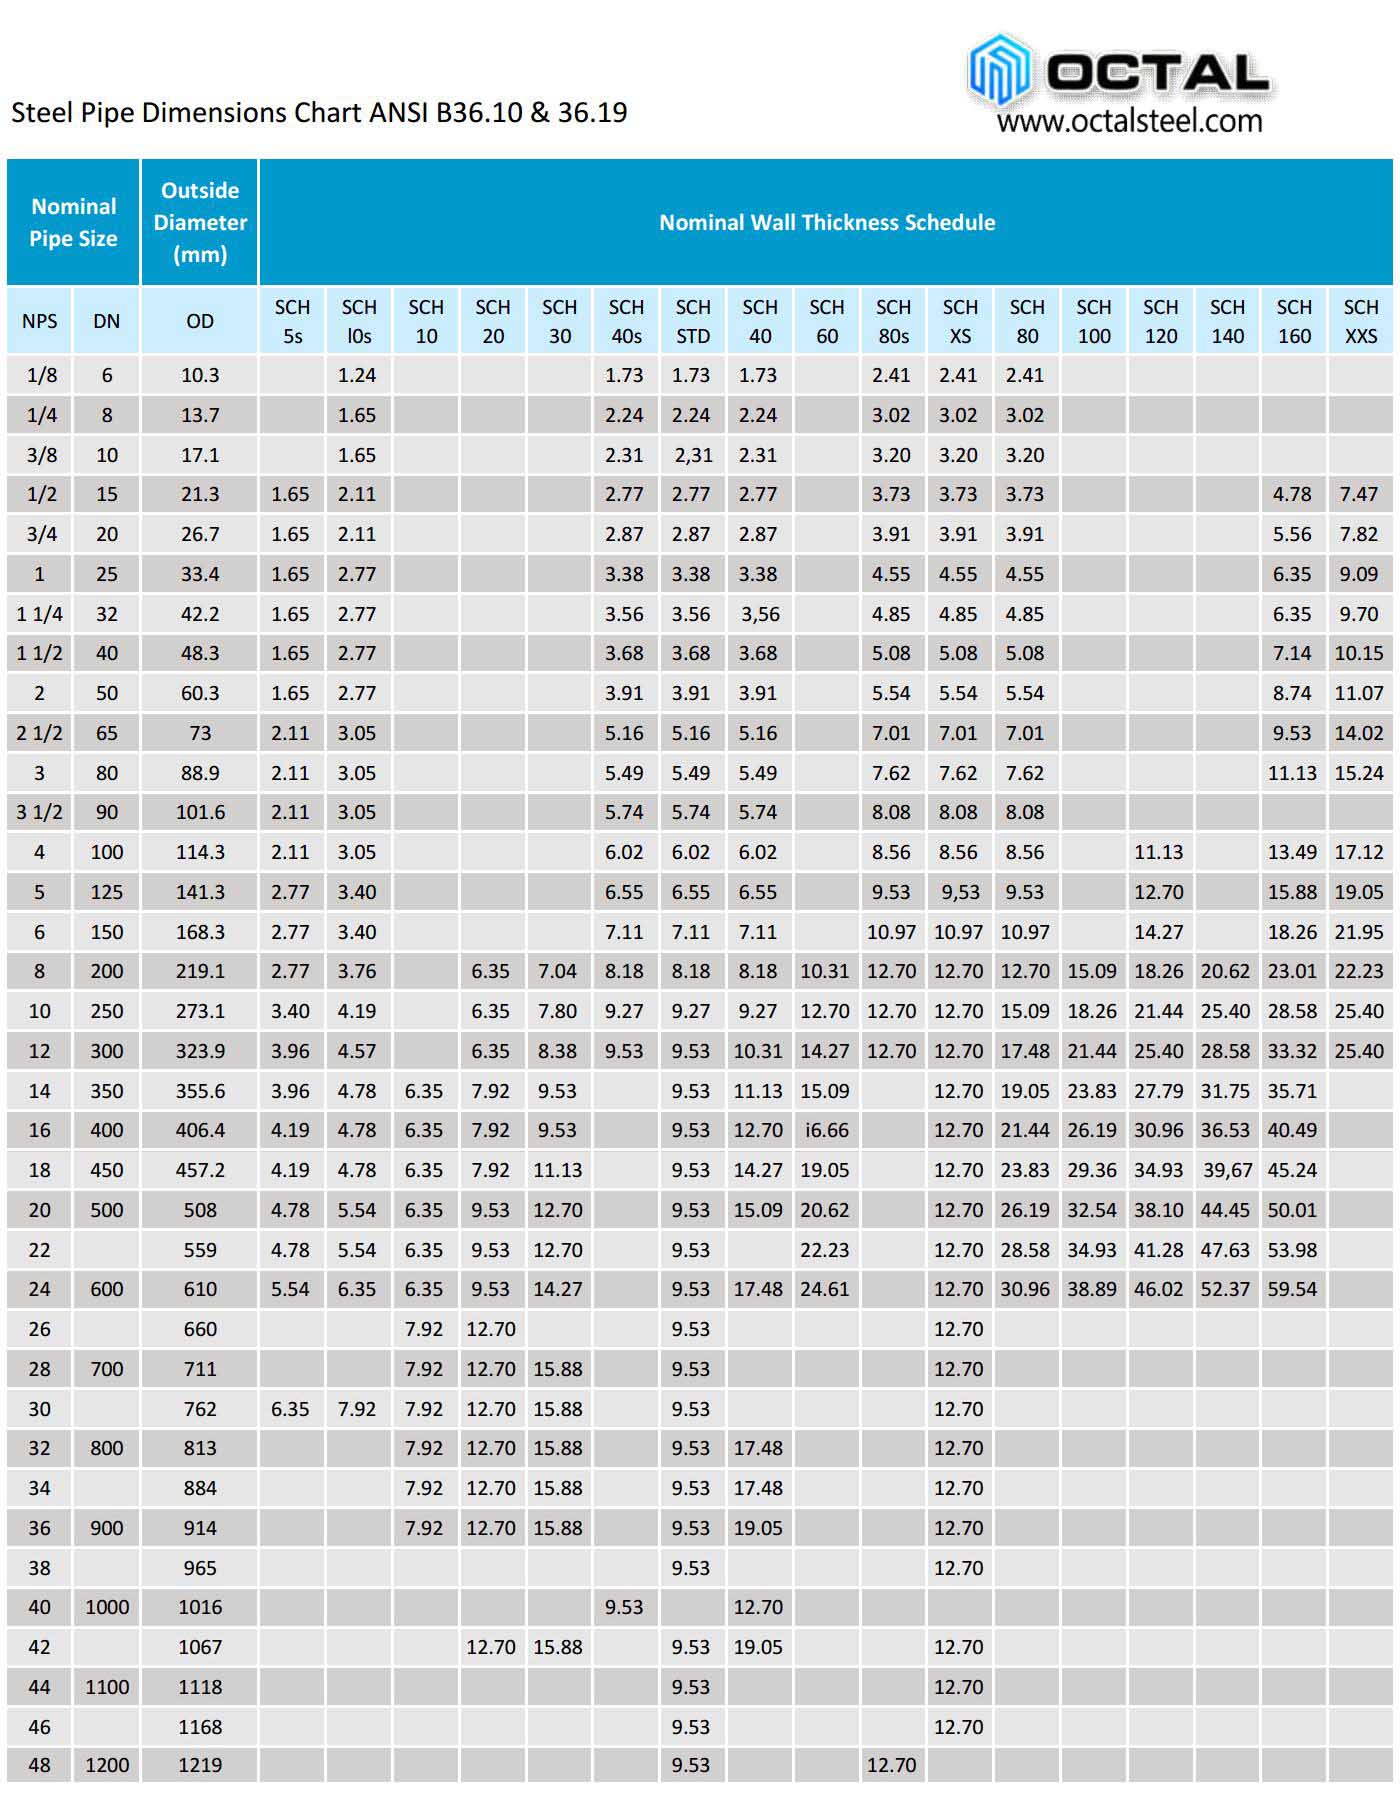
Dn Standard Pipe Size Chart
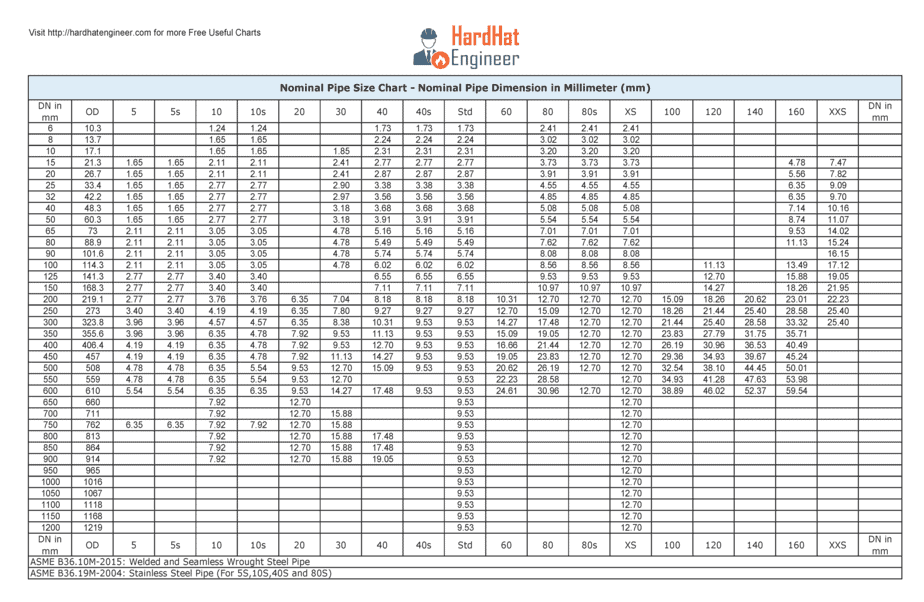
Dn Standard Pipe Size Chart
DN Nominal Pipe Size Chart Metric MM PDF
DN Nominal Pipe Size Chart Metric MM PDF
Conversion Table for Diameter Nominal (DN) to Inches
If Openca Behaves Like Most Ldap Aware Applications, This Is What Is.
How Can We Use A Dn Attribute In An Ldif File If Dn Is Not Defined In Any Schema?
Why Is Distinguishedname Commented Out?
I Cannot Instantiate A New Directoryentry Because Then I Would Have Have To Either Use The.
Related Post: